


Solana Bot Bloom Hacked for $947K: 49 Wallets Drained
Bloom Trading Bot Hit by $947,000 Exploit
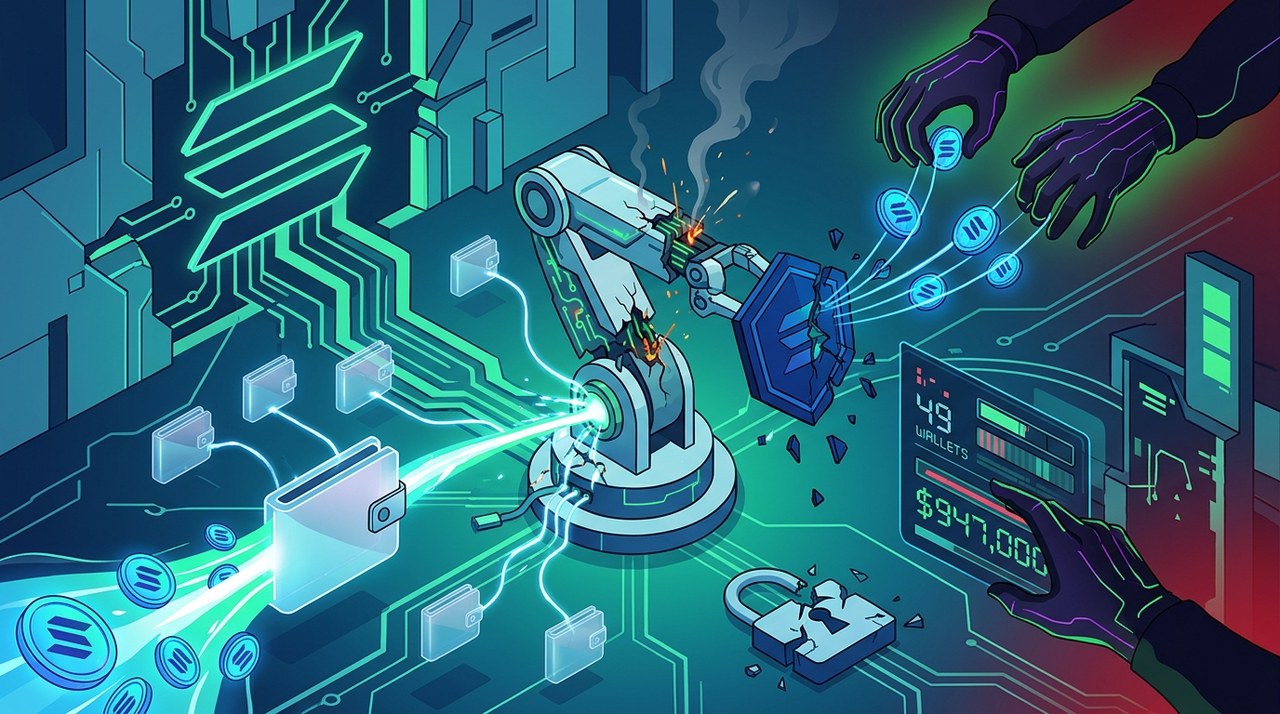
Imagine waking up to find your crypto trading bot opened the digital doors to a hacker. On October 26, 2026, popular crypto trading platform Bloom experienced a major security breach. A hacker managed to drain 9,408 SolanaSOL-1.31% tokens from customer wallets. At the time of the attack, the stolen cryptocurrency was valued at approximately $947,000.
Early blockchain data estimates placed the total damage slightly higher at around $954,000. Blockchain monitoring account Onchain Lens was among the first to flag the suspicious transfers on-chain. Soon after, Onchain Alert reported that the attacker consolidated funds into a known drainer address, posting a warning on X: "A hacker drained 9,408 SOL from 49 victims in one of its drainer [wallets], final number might be much higher."
The monitoring accounts pointed out that the single largest individual wallet drain took away 1,636 SOL, which was worth roughly $166,000. Interestingly, the attacker focused almost entirely on SOL holdings while leaving stablecoin balances like USDCUSDC-0.15% untouched.
Past performance of digital assets is not an indicator of future performance. Digital asset markets are subject to high price volatility.
Bloom Clarifies Victim Count and Explains the Vulnerability
While early reports suggested 49 separate victims were affected, Bloom's internal investigation revealed a key detail. The attack actually targeted 49 wallet addresses owned by just nine individual users.
Bloom operates as a Telegram-based trading bot that supports both Solana and EthereumETH-1.82% Virtual Machine (EVM) networks. Naturally, users immediately worried that their private keys had been leaked. However, Bloom reassured the community that private keys remained completely secure.
Instead of stolen keys, the entry point was a complex third-party software flaw known as a Remote Code Execution (RCE) vulnerability. An RCE exploit allows an attacker to manipulate software code remotely without directly extracting seed phrases or private keys. Still, this leaves a tough technical question unanswered: if private keys were not exposed, how did third-party software gain permission to move nearly $1 million?
Immediate Shutdown and Operational Next Steps
To prevent any further losses, Bloom took all systems offline as a security precaution while technical teams investigated the issue.
"All Bloom systems are currently offline as a precautionary security measure. Once services are safely restored, we will announce it through our official channels. At that point, all users will be required to log in again to Bloom Manager and the Chrome Extension to resume using Bloom normally. Thank you for your patience and understanding,"
The team advised affected customers to immediately create brand-new wallets and transfer any remaining funds out of old addresses as soon as possible.
Bloom Pledges 100% Reimbursement for All Losses
In positive news for impacted users, Bloom announced it will cover the entire financial loss. The company committed to restoring every single stolen token.
Bloom publicly stated: "Bloom will fully reimburse 100% of the stolen funds directly to secure wallets designated by the affected users."
Beyond issuing refunds, Bloom is actively tracing the stolen cryptocurrency across the blockchain, working on potential freezing options, and attempting to uncover the attacker's identity. The project highlighted its experience in the industry, noting that its core team has built software since 2018 and traded in crypto markets since 2021. As of now, Bloom has not provided a specific timeline for when reimbursements will be completed or when the platform will reopen.
What This Incident Means for Crypto Automated Trading
This security breach comes amid a broader wave of smart contract bugs, data leaks, and exploits across the web3 industry. Some analysts have pointed to the rising use of artificial intelligence (AI) coding assistance as a potential factor behind subtle software vulnerabilities.
For traders using automated bots, this event serves as a clear reminder of the technical risks involved in connecting wallets to third-party tools. Rigorous security practices, external audits, and careful software management remain critical elements for protecting user assets.
Latest blog posts
SpaceX Secures $40B AI Deal as Musk Warns Neoclouds
SpaceX lands a $40 billion GPU financing deal, while Elon Musk warns that over 200 AI chip rental firms face major financial trouble.
|

Ex-DOGE Staffers Breach Anthropic via Bug Bounty
Four former DOGE employees created cybersecurity startup Cathedral and found security gaps at Anthropic using AI agents.
|

Electrum Patches Wallet Bug That Hijacked Bitcoin Fees
Electrum released version 4.8.3 to fix a severe bug that allowed rogue servers to inject fake transactions and steal user funds via fee-bumping.
|