
Electrum Patches Wallet Bug That Hijacked Bitcoin Fees
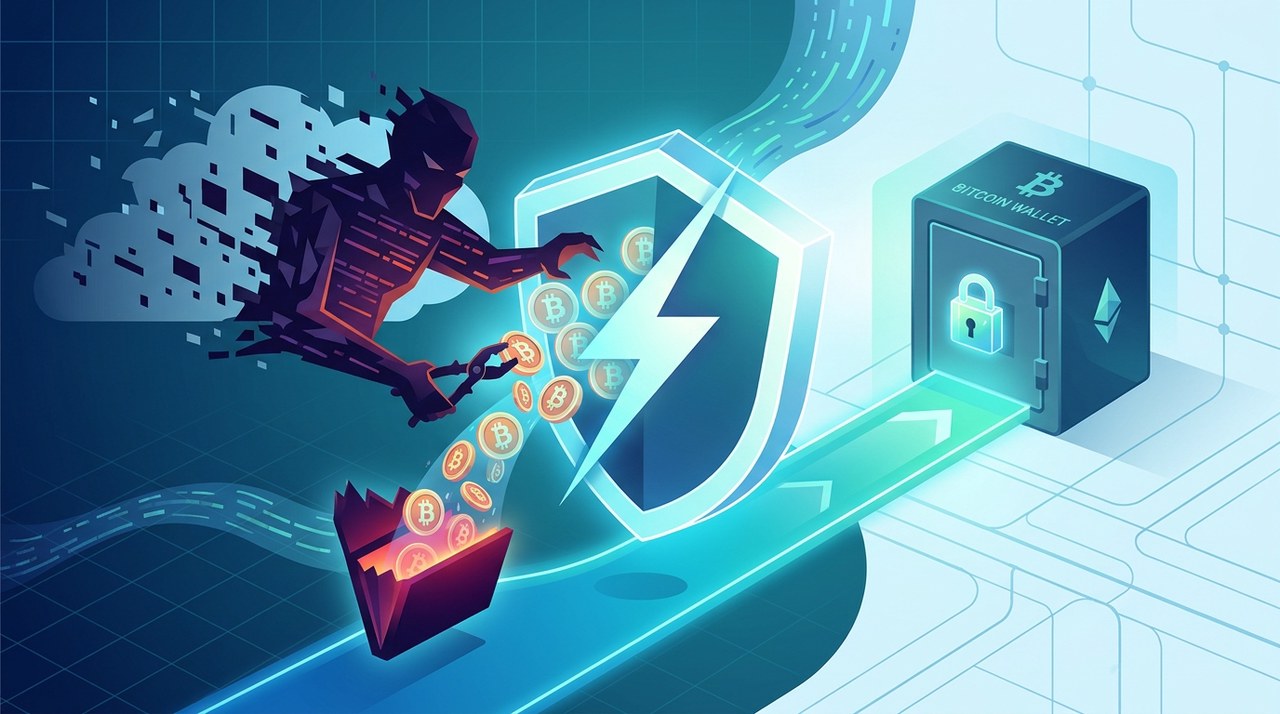
An Urgent Security Update for Electrum Users
If you store your BitcoinBTC-0.64% in the popular Electrum wallet, you should check your app version right away. Electrum released version 4.8.3 on October 24 to patch a high-severity security flaw.
This vulnerability allowed malicious servers to tamper with pending transactions. By tricking users into boosting fees on seemingly stuck payments, attackers could secretly redirect Bitcoin straight into their own crypto addresses.
The bug impacts all Electrum wallet versions released before version 4.8.3. Sadly, at least one user has already lost funds because of this exploit.
How the Rogue Server Attack Works
To understand how this hack works, it helps to look at how Electrum talks to the Bitcoin network. Electrum is a lightweight wallet. Instead of downloading the whole blockchain, it relies on external public servers to get data and broadcast payments.
Think of these servers like post offices handling your letters. If you accidentally connect to a rogue post office, it can manipulate what you see in your mailbox.
Here is how a rogue server pulls off the trick step by step:
- You send a normal Bitcoin payment through a compromised server.
- The rogue server hides your real transaction so the network never receives it.
- The server sends back a fake unconfirmed transaction showing a zero transaction fee and an attacker address.
- Your wallet shows the payment as stuck or unconfirmed due to the missing fee.
- You use the built-in fee-bumping feature to increase the transaction fee and push it through.
- When you approve the fee-bump, you sign a completely new valid transaction that pays the attacker instead of your real recipient.
Because your initial payment was never actually broadcast, your fee-bump becomes the first real transaction to hit the network. It signs over your money directly to the hacker.
Address Spoofing: Matching the Last Four Characters
Bitcoin addresses are long strings of numbers and letters. Many people only check the first few or last few characters of an address before hitting send.
Electrum developer Somber Night published the official advisory and explained a sneaky tactic attackers used called address grinding.
The hackers generated thousands of fake Bitcoin addresses until they created one that matched the final four characters of the victim's intended destination. If you only glanced at the tail end of the address, the fake transaction looked completely legit.
Real Victims and Reports in the Wild
The official advisory confirmed that rogue servers have actively executed this attack on real users.
A user named dannydeezy first spotted suspicious server activity on October 11. In that instance, the tampered transaction failed to spread beyond the local server, so no funds were stolen.
Unfortunately, a second user named Raju-K12 was not as lucky. On October 18, Raju-K12 confirmed a financial loss after fee-bumping a transaction that had been secretly altered by a malicious node.
How Electrum 4.8.3 Fixes the Vulnerability
The Electrum developer team moved fast to patch the core security flaw. They tagged the fix in their public repository on October 23 and published updated app files on October 24.
Version 4.8.3 fixes the problem by verifying cryptographic signatures on all wallet-owned inputs before adding any unconfirmed transaction to your transaction history.
In plain English, a bad server can no longer trick your wallet with fake transactions linked to your funds. The server cannot fake your digital signature, so the wallet immediately rejects the bad data.
A Remaining Limitation with Incoming Payments
While version 4.8.3 protects your outgoing funds, developers noted that one small limitation remains.
Incoming transactions sent from external wallets—where none of the input addresses belong to your wallet—are still accepted without signature verification.
Developer Somber Night acknowledged this gap in the advisory, explaining that completely fixing external incoming transactions will require extra developer work in future updates.
Electrum's History with Open Server Attacks
Electrum is one of the oldest and most respected Bitcoin wallets, but its open design comes with unique risks.
Electrum uses an open server model where anyone can set up and run a node. While this keeps the network decentralized, it also means bad actors can run public servers designed to attack users.
This is not the first time hackers have targeted Electrum's server model. Back in 2018, attackers used rogue servers to pop up fake software update notices. By 2020, those phishing scams had stolen an estimated $25 million from users.
How You Can Keep Your Bitcoin Safe
If you use Electrum, here are the essential steps to keep your funds secure:
- Update immediately: Download version 4.8.3 directly from the official electrum.org website or their official GitHub repository.
- Run your own server: Users who connect Electrum exclusively to their own private node are completely safe from this server attack.
- Verify full addresses: If you cannot update right away, manually inspect every character of your recipient's address and the fee amount before approving any fee-bump.
Staying informed and double-checking payment details remains the best way to safeguard your self-custody crypto wallet.
Latest blog posts
NBA Names Kalshi and Polymarket Preferred Exchanges
The NBA has designated Kalshi and Polymarket as preferred prediction platforms while establishing CFTC safeguards against insider trading.


Ripple Treasury Launches 24/7 AI Platform Using RLUSD
Ripple Treasury has introduced an AI-powered platform to keep corporate cash active 24/7 using the RLUSD stablecoin.
|

Lula Win Keeps Brazil Gambling Ban Active as Licenses Expire
Brazilian President Lula secured a surprise runoff win as 85 gambling licenses expired without refunds, reaffirming his hardline stance on online betting.
|