
Electrum Bug: How Rogue Servers Stole Bitcoin via RBF
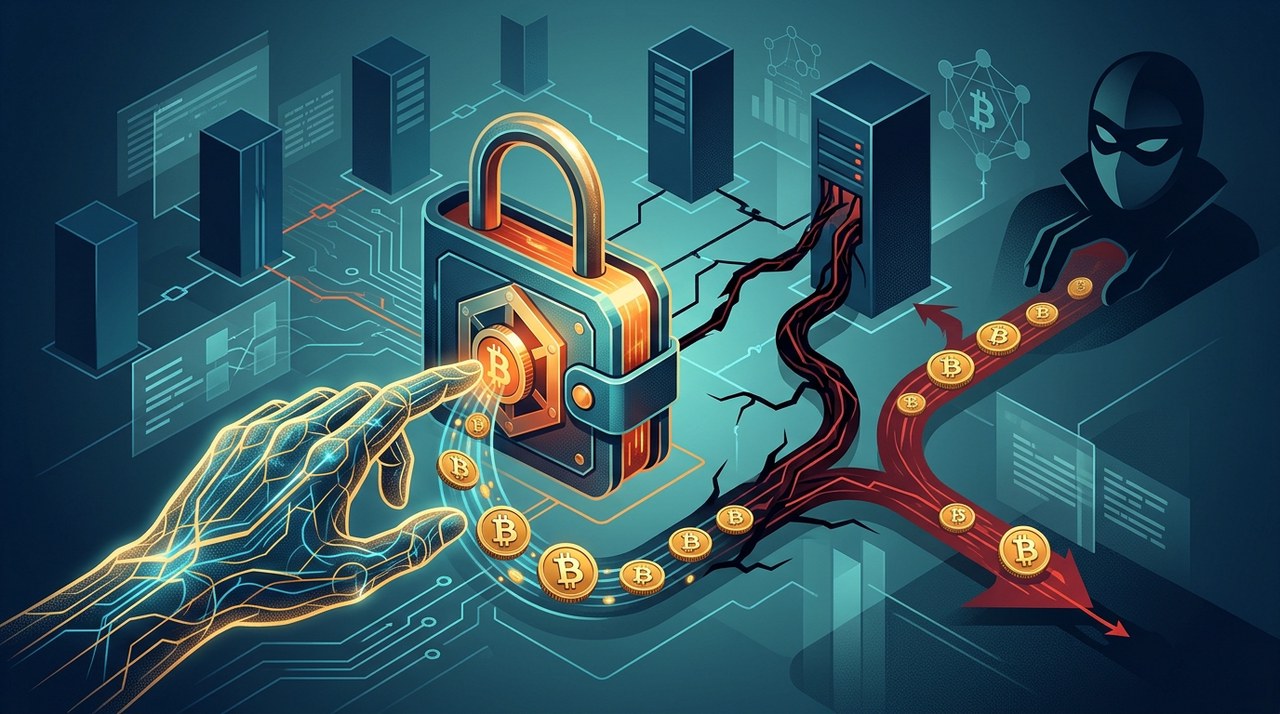
A Sneaky Security Flaw in a Trusted BitcoinBTC-0.47% Wallet
Imagine trying to speed up a stuck Bitcoin transaction, only to accidentally send your hard-earned funds straight to a scammer. That exact nightmare scenario recently came true for at least one crypto user due to a security flaw in Electrum, one of the oldest and most popular Bitcoin wallet applications.
The vulnerability allowed malicious servers to trick Electrum users into signing unauthorized payments. Developers confirmed the issue after receiving reports from affected users, prompting an immediate patch in Electrum version 4.8.3 released on October 24, 2026.
Understanding How Electrum Works
To understand how this exploit happened, it helps to look at how Electrum operates. Unlike full Bitcoin nodes, which download the entire blockchain history to verify every transaction independently, Electrum is a lightweight wallet. It relies on remote servers to fetch transaction history and broadcast new payments to the network.
Electrum relied on outside servers to retrieve transaction histories. Before the latest fix, the software trusted those servers without checking if signatures on pending payments were actually valid.
Because previous versions of Electrum did not verify signatures on unconfirmed pending transactions reported by servers, a rogue server could manipulate what the user saw inside their wallet interface.
How Scammers Used Replace-by-Fee (RBF) as a Trap
The attack specifically exploited a popular Bitcoin feature called Replace-by-Fee (RBF). RBF allows users to re-send an unconfirmed transaction with a higher fee so miners prioritize processing it faster.
Here is how the exploit played out step-by-step:
- Intercepting the original payment: When a user created a valid transaction, a malicious server intercepted it before it reached the main Bitcoin network.
- Replacing it with a fake transaction: The bad server inserted a fraudulent transaction into the wallet's history, redirecting funds to an attacker's address using invalid signatures.
- Simulating a stuck payment: The fake transaction was often set up with zero network fees, making it appear to the user as if their payment was stuck indefinitely.
- Tricking the user into using RBF: Feeling impatient, the user selected the Replace-by-Fee option inside Electrum to increase the fee and speed up delivery.
- Signing the real transfer: Electrum took the fake server-provided transaction and generated a brand-new, valid signature authorizing the transfer of actual coins directly to the hacker.
Visual Tricks Made Detection Harder
To make the fake transaction even harder to notice during a quick check, attackers created receiving addresses where the last four characters matched the original destination address. Users doing a quick glance at the beginning or end of an address could easily miss the swap.
Timeline of Incident Reports
Electrum developers received two distinct user reports in October 2026 revealing how rogue servers were exploiting the flaw:
- October 11, 2026: A user with a two-of-three multisignature wallet using two Trezor hardware devices noticed a suspicious outgoing transaction in their wallet history after checking their payment. Fortunately, this user did not report losing any funds.
- October 18, 2026: A second user reported bumping the fee on what appeared to be a pending transaction, unknowingly signing the attacker's fake transfer and losing money as a result.
While developers have not disclosed the exact total amount stolen or identified the malicious servers involved, they acted swiftly to issue a code repair.
How to Stay Protected
Electrum released version 4.8.3 on October 24, 2026, which forces the wallet to verify cryptographic signatures on unconfirmed transactions before displaying them or allowing fee modifications. If you use Electrum, here are essential steps to keep your funds safe:
- Update immediately: Ensure your Electrum wallet is running version 4.8.3 or higher. Older versions remain vulnerable when connected to unknown servers.
- Verify full addresses: Always check every single character of a destination address, not just the first or last few characters.
- Use trusted nodes: If you run your own Bitcoin node or connect exclusively to trusted private servers, you were not exposed to this public server attack.
Navigating Bitcoin Security and Market Realities
Software bugs are a stark reminder that self-custody requires ongoing vigilance and keeping software up to date. Security events often coincide with broader market volatility, such as Bitcoin price fluctuations around macroeconomic events.
Past performance of digital assets is not a guarantee of future performance. Market conditions can shift rapidly, making careful risk management and secure storage habits essential for all crypto users.
Latest blog posts
Musk Warns 200 AI Neoclouds Face Extinction
Elon Musk warns over 200 AI neocloud startups face a 'guppy-level death' as Gartner predicts 80% of specialist cloud providers will disappear by 2030.

US Allocates $5M to Track Illicit Crypto in the Pacific
The U.S. government launched a $5 million program to train Pacific island law enforcement in tracking illegal cryptocurrency transactions.
|
Why CoreWeave Is Facing Major Debt Pressure
CoreWeave stock has fallen nearly 40% as investors worry about $52 billion in debt, despite doubling its quarterly revenue.
|