
XRPL Discloses Critical Fix for Bug That Could Create XRP
A Quick Look at What Happened
Developers behind the XRPXRP+0.81% Ledger recently shared details about two software vulnerabilities that were discovered and patched.
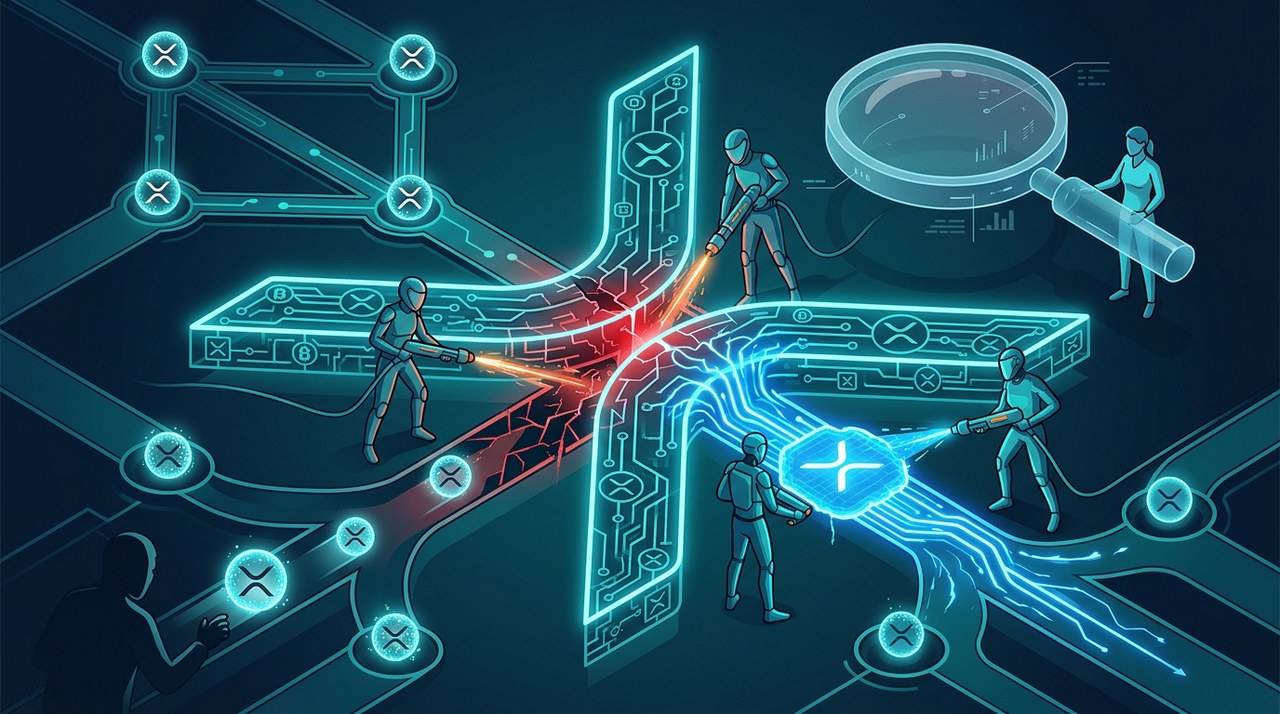
The most severe issue was a critical bug in the ledger payment engine that could have allowed an attacker to create brand-new spendable XRP.
The second issue involved a new transaction feature that could have caused server disagreements during transaction processing.
Fortunately, security researchers and developers caught both problems early. Official reports confirm that no funds were stolen and no public networks were exploited.
Understanding the Critical Payment Engine Bug
Blockchain networks rely on precise arithmetic to keep token supplies strictly controlled.
On October 9, 2026, the XRP Ledger team publicly detailed a flaw in how its payment engine calculated transactions across multiple offers.
This specific bug occurred inside the built-in decentralized exchange order book on the network.
How Order Books Process Trades
Think of an order book as a digital marketplace board listing buy and sell orders.
When a large trade occurs, the payment engine may route the transaction through many individual offers to fill the total request.
During this routing process, the engine continuously calculates the total XRP required to complete the path.
What Caused the Calculation Overflow?
The vulnerability triggered what software engineers call a numerical calculation overflow.
You can picture an old mechanical odometer reaching its maximum limit and resetting back to zero.
When combined trade values exceeded the maximum number supported by the software code, the calculation rolled over.
As a result, the payment engine charged the buyer less XRP than the total amount credited to the sellers.
That accounting gap effectively allowed new, spendable XRP to appear out of nowhere.
How the Bug Bounty Program Caught the Flaw
An independent security researcher discovered the payment calculation flaw and reported it through the XRPL Bug Bounty program on September 22, 2026.
Triggering the bug was far from simple and could never happen by accident.
An attacker needed to craft a complex setup featuring hundreds of order book offers set at unusually high prices.
They then had to execute a carefully structured payment transaction to force the calculation overflow.
Standard trades and everyday payments were entirely unaffected by this flaw.
The Quick Response from Engineers
Engineers at RippleX quickly recreated the vulnerability in a controlled environment to study its behavior.
They confirmed that any newly generated XRP could have been spent if the attack succeeded.
Developers released a patch in xrpld version 3.4.1 on September 25, 2026.
The update added strict validation steps to prevent calculation overflows and secured the system against unauthorized token creation.
The disclosure confirmed that no public network experienced any unauthorized token creation from this issue.
The Second Bug: Batch Transaction Validation
The disclosure report also detailed a separate issue related to the XRPL Batch transaction feature.
Batch transactions allow users to bundle several transactions together into a single submission, saving time and simplifying complex actions.
How the Batch Structure Caused Risk
The flaw allowed a transaction inside a batch to contain an improperly structured field.
Even though the field contained errors, the server software still accepted and processed the transaction.
This created a scenario where different software versions running across the network might evaluate the transaction differently.
Protecting Network Consensus
In a decentralized network, every validator node must reach total agreement on ledger history.
If servers disagree on whether a transaction is valid, validators cannot reach consensus.
Disagreements like this can pause transaction validation and slow down overall ledger operations.
The report made clear that this flaw did not allow attackers to steal funds or bypass digital signatures.
Fixing the Batch Feature Before Mainnet Launch
Crucially, the Batch transaction feature was not active on the XRPL mainnet when researchers identified the issue.
Because the feature was inactive on the live network, no user accounts or real funds were ever put at risk.
Resetting the Amendment Timeline
To address the issue properly, developers and validator operators temporarily withdrew support for the original Batch amendment.
This action reset the activation timeline while engineers created a updated proposal called fix Batch V1_2.
The updated amendment enforces strict structural formatting rules for all bundled transactions.
The corrected amendment gained full network support and officially activated on the mainnet on October 9, 2026.
Strengthening Security Procedures for Future Releases
Alongside software updates, the XRPL development community introduced changes to their security testing framework.
Engineers now plan to retest all reported vulnerabilities against release candidates before any software goes live.
This extra layer of verification helps confirm that all patches work as expected before code reaches node operators.
What XRP Holders Need to Know
If you hold XRP in a self-custody wallet or on an exchange, you do not need to take any action.
You do not need to move your funds, update your wallet software, or change your private keys.
Neither vulnerability led to any loss of assets, and the total circulating supply of XRP remained completely unchanged.
Instructions for Node Operators
While regular users can rest easy, the software updates are essential for individuals and organizations running XRPL servers.
Server operators must update their nodes to xrpld version 3.4.1 or newer to maintain compatibility and stay synchronized with the network.
Key Timeline of Events
- September 22, 2026: Security researcher reports the payment engine overflow issue via the XRPL Bug Bounty program.
- September 25, 2026: RippleX releases xrpld version 3.4.1 with a complete fix for the payment engine calculation bug.
- October 9, 2026: Official disclosure report is published, and the fix Batch V1_2 amendment officially activates on mainnet.
- Public Impact: Zero funds lost and zero unauthorized XRP created across all public ledger networks.
Latest blog posts

Cardano Midnight Secures Major Exchange Listing in Japan
Cardano-linked privacy network Midnight is expanding in Japan as its NIGHT token secures a new listing on OKCoin Japan starting October 13, 2026.
|


 +1
Bitcoin ETFs See $680M Outflows as Inflow Streak Ends
Spot Bitcoin ETFs recorded $681.10 million in weekly net outflows, breaking a three-week streak of positive institutional inflows.
|

BTC and ETH Rebuild Liquidity 1 Year After Crash
One year after the historic October 2025 crypto flash crash, Bitcoin and Ether order books have recovered strongly while altcoins continue to lag behind.
|