
PHP Flaws Trigger Millions of Cyberattacks Worldwide
What Is Happening with PHP Right Now?
Imagine waking up to find out that the lock on millions of front doors around the world suddenly stopped working. That is essentially what happened to the internet this week.
Cloudflare CEO Matthew Prince issued a stark warning after security teams detected a massive surge in cyberattacks targeting two critical security flaws in PHP.
For those unfamiliar, PHP is one of the most common building blocks of the web. According to data from W3Techs, PHP powers around 69% of all websites with a known server-side programming language.
Millions of Attacks in Just a Few Hours
Cybercriminals did not waste any time taking advantage of these flaws. The sheer speed of the onslaught shocked cybersecurity experts around the globe.
On October 22, 2026, Cloudflare CEO Matthew Prince shared troubling statistics on X about how fast the attacks escalated:
Some stats on #php2shell. In the 10 hours before it was publicly announced, across the @Cloudflare network we saw thousands of attempts to exploit it. That jumped to tens of thousands in the 45 minutes post announcement, hundreds of thousands within 2 hours, and millions now.
These two flaws are collectively known as PHP2Shell. Their official security tracking numbers are CVE-2026-109618 and CVE-2026-109619.
Both flaws received a Common Vulnerability Scoring System (CVSS) score of 9.2 out of 10, marking them as extremely critical. What makes them so dangerous is that attackers can run malicious code on a vulnerable server without needing to log in first.
Interestingly, researchers actually discovered these flaws with the help of AI research tools. However, as soon as the weaknesses became public, hackers rushed to exploit them.
Global Agencies and World Leaders Issue Urgent Warnings
The threat is so severe that law enforcement agencies and world leaders are stepping in directly to warn website operators.
The FBI's CyberCYBER-2.70% Division issued an urgent advisory warning that criminals could use these vulnerabilities to execute remote code, potentially exposing sensitive networks and private user data.
Government authorities across the United States, the United Kingdom, and Japan have issued clear instructions to system administrators:
- Install official security updates immediately.
- If you cannot patch right away, take affected systems offline until they are secure.
Japan's Prime Minister, Sanae Takaichi, also personally urged website operators across the country to double-check their PHP systems without delay.
A Wave of Security Incidents Over the Last 48 Hours
The PHP warning comes during a particularly chaotic week for online safety. Several other serious security incidents broke out over the past 48 hours:
- GitLab Maximum Vulnerability: Developer platform GitLab disclosed a maximum-severity flaw scored 10 out of 10.
- LiteLLM Code Poisoning: Reports surfaced that LiteLLM contained password-stealing code.
- AI-Powered Attacks: Hackers allegedly used AI tools to attack over 1,200 websites and 100+ companies, including major industrial names like John Deere and Cummins.
- eMudhra Key Weakness: India's eMudhra revealed that eight intermediate certificate keys were dangerously weak. One key was set to the single number '4', raising concerns about more than 60 million digital certificates.
- State Bank of India Data Leak: SBI confirmed that 3,897 customer records recently appeared on the dark web.
What Should You Do to Protect Yourself Today?
Whether you run web servers, manage automated crypto trading bots, deploy AI agents, or use third-party platforms, taking defensive measures immediately is critical.
Here are the recommended steps to safeguard your infrastructure:
- Update PHP immediately: Anyone running affected PHP versions should install the official security patches right away.
- Check for signs of breach: Review system logs for unauthorized activity or unauthenticated access.
- Utilize Web Application Firewalls: Cloudflare has deployed automated protective rules for its WAF customers, but the company stresses that patching remains mandatory.
- Audit external crypto and AI tools: Ensure your automated trading bots, Web3 platforms, and API integrations are not hosted on unpatched PHP servers.
Latest blog posts

XRP Ledger Bug Fix Delayed to Nov 4 After Validator Blip
A minor technical delay has pushed back the activation of the XRP Ledger's latest bug fix amendment to November 4 after a brief drop in validator votes.
|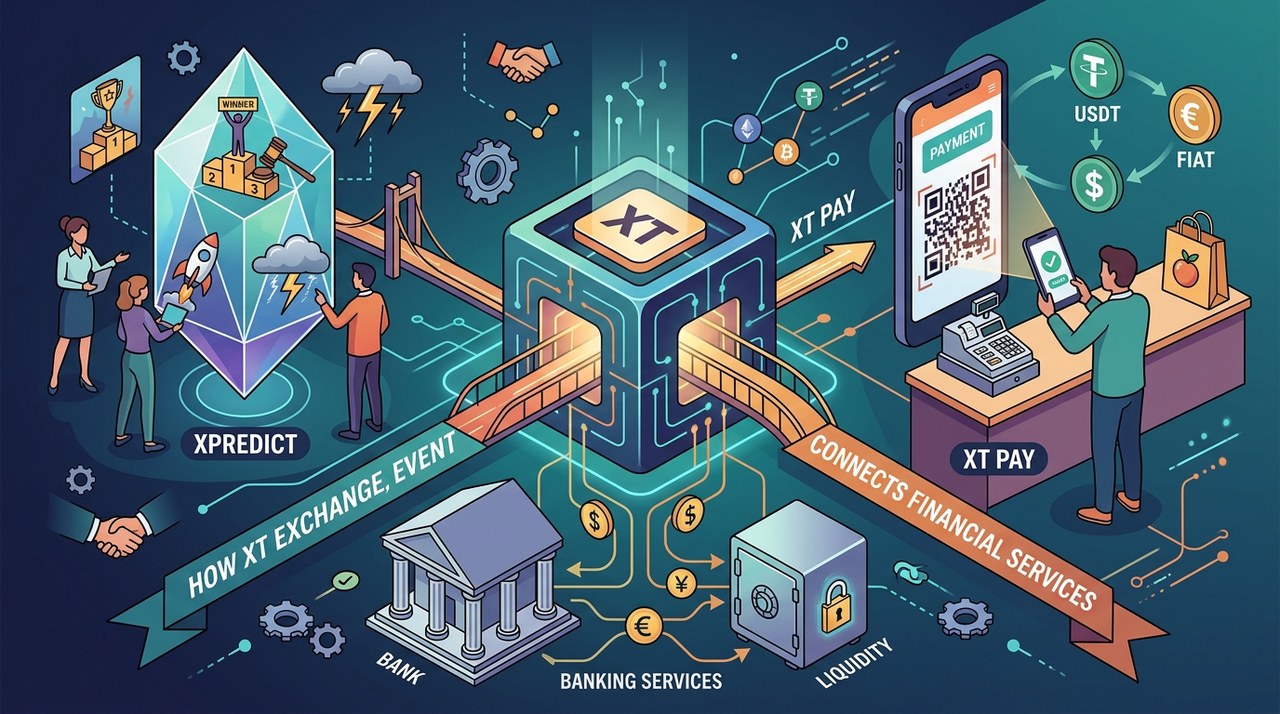
How XT Exchange Connects Financial Services
XT Exchange leverages third-party integrations like Polymarket and local payment providers to expand its trading features and payment services.


Bitmine Near 5% ETH Cap as Tom Lee Outlines Next Phase
Bitmine is approaching its self-imposed 5% Ethereum holdings cap. Chairman Tom Lee explains what comes next for its corporate treasury and the broader market.
|