Ledger Reseller Breach Expands Amid $200M Cold Wallet Attacks
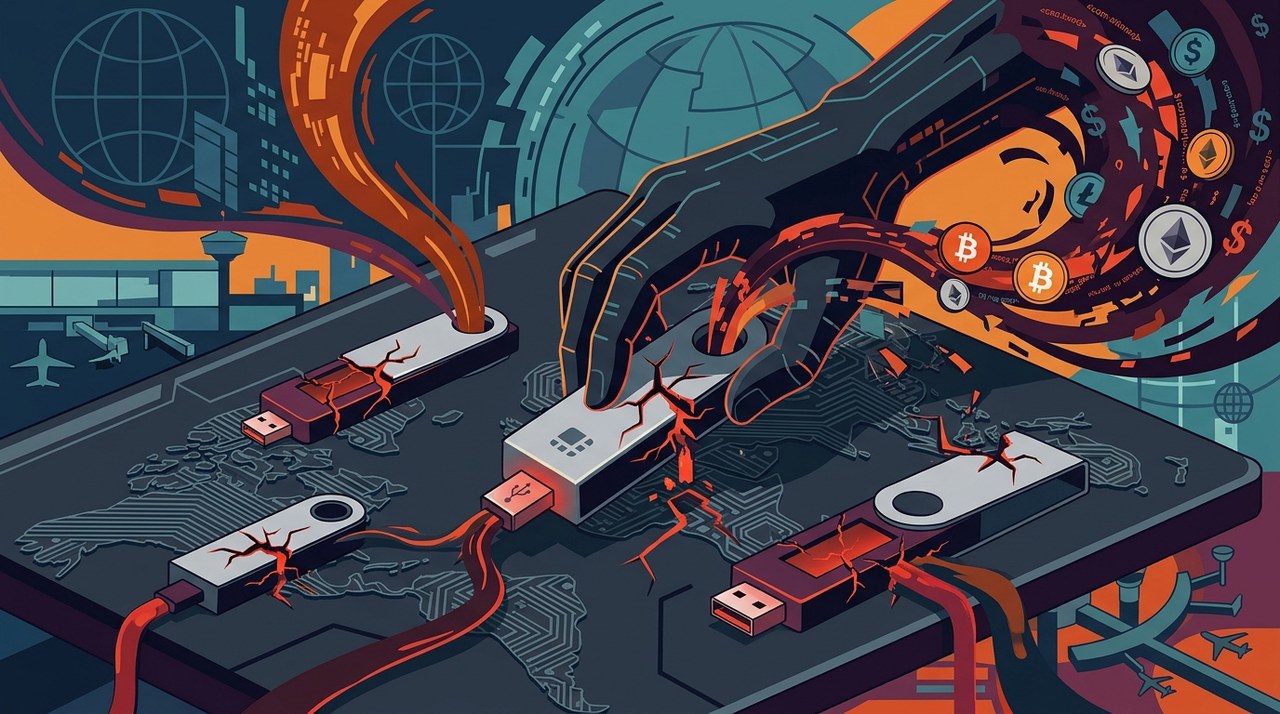
Ledger Reseller Breach Escalates Across Global Markets
On October 9, the crypto community experienced a major security incident involving Ledger hardware wallets. A supply chain attack resulted in crypto theft with total losses exceeding $90 million, with some estimates reaching around $93 million. Hardware wallets are designed to keep private keys offline and safe from online hackers. However, when physical hardware is altered before reaching a buyer, offline protections can be compromised.
Initial reports pointed to a single compromised source: Southeast Asian retailer Crypto Bilis. However, new findings reveal that the issue is significantly broader than first understood. At least four officially recognized retail vendors have now been confirmed to have distributed tampered Ledger products to unsuspecting customers.
The Four Official Resellers Identified with Compromised Hardware
What makes this incident particularly concerning for users is that every compromised store was explicitly listed on Ledger's official website as a legitimate distributor. Below is the detailed breakdown of the affected retail outlets across Asia and Europe.
1. Meta Pod (Asian Airport Locations)
Meta Pod is a retail brand operating inside major international airports across Asia, including busy travel hubs in Hong Kong and Malaysia. Investigators confirmed that a Ledger Flex device bought at a Meta Pod location was infected with malicious code before purchase.
2. Challenger (Singapore)
Challenger is a well-known electronics retail chain in Singapore. Security researchers traced a tampered Ledger Flex device back to its store in Vivo City. CryptoQuant analyst Darkfost had previously marked Challenger as high-risk due to its geographical proximity and logistics ties with Crypto Bilis.
3. Media Markt and Saturn (Europe)
The supply chain threat extends into Europe through the major electronics retail chain Media Markt Saturn. A Ledger wallet purchased from Media Markt Saturn was confirmed to be infected with malicious code. Meanwhile, another unit bought at Media Markt Trier is currently under active investigation for physical interference.
Both European retail locations receive their inventory from Aqipa GmbH. This European electronics distributor has handled the distribution of Ledger hardware wallets in Germany and Austria since August 2023.
4. Reseller Suspensions and Distribution Safeguards
In response to these findings, Ledger suspended sales and shipping services for both Crypto Bilis and Media Markt/Saturn. Security analysts are closely monitoring additional official resellers that share regional proximity or distribution partners like Aqipa GmbH.
Security Analysts Criticize Ledger's Incident Handling
The security breakdown has drawn sharp criticism from on-chain researchers and community members. CryptoQuant analyst Darkfost publicly accused Ledger of being slow to respond to critical threats. Darkfost highlighted that independent on-chain analysts identified the supply chain danger well before Ledger published official warnings.
Furthermore, community members pointed out that independent social media accounts on X were providing clearer guidance on wallet verification than the company itself. Added to this frustration was Ledger's refusal to cover return shipping fees for customers sending back recalled devices for verification.
Hardware Wallet Losses Pass $200 Million in 2026
The Ledger supply chain incident is part of a larger trend of hardware wallet security events that have collectively resulted in over $200 million in losses this year. These incidents span hardware implants, software vulnerabilities, and data privacy breaches.
Post-Production Implants and Ownership Changes
The compromised Ledger devices involved physical implants installed after factory manufacturing. Investigators believe this attack vector was enabled by an unannounced ownership change at Crypto Bilis in early August, which allowed bad actors to manipulate hardware before distribution.
Coldcard Software Bug ($116 Million Drained)
Supply chain attacks are not the only threat hitting cold storage users. In July, hackers exploited a software vulnerability in Coldcard wallets, leading to a massive loss of $116 million across affected user accounts.
Tangem Wallet Vulnerability Test
Tangem wallet made headlines when researchers subjected its card-style wallet to advanced laser fault-injection tests. While no customer funds were stolen or lost during the experiment, the successful demonstration disproved the marketing narrative that the devices were completely unhackable. In a notable twist, the security flaw was discovered by Donjon, which is Ledger's internal security research team.
Data Privacy Leaks at SafePal and Trezor
Physical security is only one part of the equation. In August, a third-party logistics network used by SafePal and Trezor suffered a data breach. The incident exposed the personal identifiable information (PII) of thousands of customers, creating potential phishing risks for hardware wallet owners.
Understanding Cold Storage Security and Risk
Hardware wallets remain a standard method for self-custody in the crypto industry, but recent events demonstrate that no single security method is completely immune to risk. Supply chains, logistics partners, and software layers each introduce distinct potential failure points.
Investors and users must stay informed about supply chain risks, verify device integrity upon receipt, and recognize that cold storage requires ongoing security precautions. Historical safety performance of any digital asset management system does not guarantee absolute safety in the future.
Past performance of digital assets or security systems is not indicative of future results. Digital asset storage and management carry inherent risks that require careful verification and risk management.
Latest blog posts
Trezor Cuts Reseller Network Following Ledger Security Breach
Hardware wallet maker Trezor is revoking authorization for many third-party resellers starting January 2027 to protect its supply chain following a major hardware attack on Ledger.


Ethereum FOMO Returns as ETF Investors Sell for 10 Days
Retail traders are turning bullish on Ethereum again, even as institutional ETF investors withdraw over $780 million.
|
Are AI Researchers Smoking to Signal Faith in AI?
A Palantir executive claims AI scientists are smoking cigarettes to demonstrate their confidence in AI curing cancer.