


Ledger Links $87M Crypto Drain to Reseller CryptoBilis
What Happened with Ledger and CryptoBilis?
If you store crypto in a hardware wallet, safety is your top priority. Recent news about draining attacks has naturally made many users nervous.
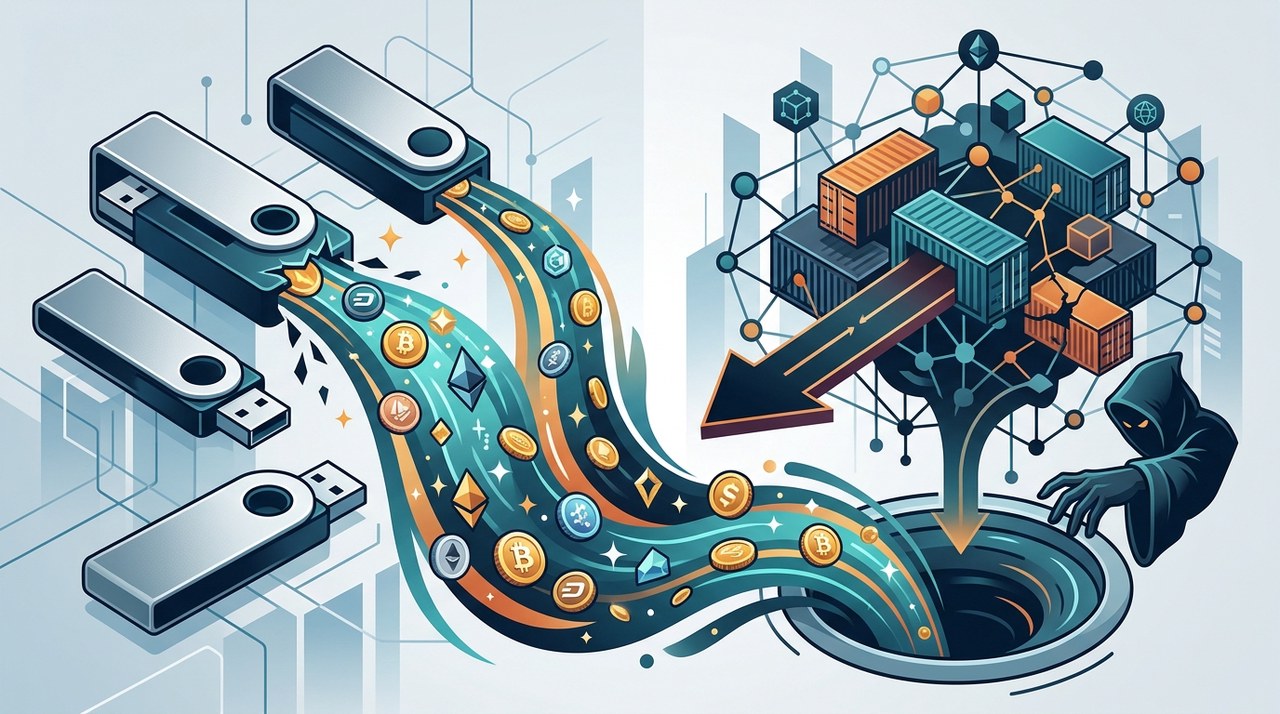
Ledger recently released a 72-hour update regarding a series of wallet drains. The company confirmed that all affected devices traced back to a single Southeast Asian reseller called CryptoBilis.
Ledger emphasized that its direct store and internal systems were not compromised. The company stated that the total number of impacted devices remains limited.
How Did the Incident Begin?
The investigation started on a Friday when users in Southeast Asia reported missing funds from newly purchased devices. Every affected user had bought their hardware through CryptoBilis.
Following the reports, CryptoBilis halted all sales of hardware wallets immediately. Ledger is now working with law enforcement agencies and contacting affected customers directly.
Onchain investigator Specter reported that over $86 million in crypto was stolen across EthereumETH-1.40%, Bitcoin, and TronTRX+0.00%. Ledger has not officially confirmed this dollar total or the exact technical method used in the breach.
Tracking the Path of Stolen Funds
Blockchain research firm YFarm X provided deeper insight into the theft. They sent Ledger a list containing details from over 450 drained wallets.
According to YFarm X, the attacker used multiple techniques to obscure their tracks on the blockchain:
- Tornado Cash: Sent 2,810 ETH through the coin mixer over three separate transactions.
- Zcash Shielded Pool: Moved funds through privacy features to break transaction trails.
- USDCUSDC+0.15% Transfers: Withdrew 3.28 million USDC into three fresh wallet addresses, making them eligible for freezing by Circle.
- USDD Swaps: Converted 15 million stolen USDT into USDD, an algorithmic stablecoin that TetherUSDT+0.12% cannot freeze directly.
- Binance Moves: Swapped 5.1 million USDD back into USDT and sent roughly 4.23 million USDT to deposit addresses on Binance.
Tether acted quickly on day one by freezing 10 million USDT linked to the attacker. However, roughly 15,475 ETH, 203 BTCBTC-1.77%, and 10 million USDD remain beyond the reach of law enforcement and issuers.
Unverified Reports in Europe
Concerns recently spread beyond Southeast Asia after an X user named Johannes reported finding tampered devices in Europe. He claimed to have bought two modified devices from retail stores.
Johannes shared images showing physical modifications inside the hardware, including additional internal cables and a hidden LTE micro-module. He urged Ledger to initiate a full product recall.
These European claims remain independently unverified. Ledger maintains that all confirmed incidents so far are limited strictly to CryptoBilis inventory. Johannes stated he is shipping the second unit to Ledger for forensic laboratory analysis.
Tightening Supply Chain Security
To prevent future tampering, Ledger issued strict directives to all authorized distributors and retail partners. The core rule is simple: never restock returned products.
When a customer returns a hardware wallet, it must never go back on store shelves. The risk of modified hardware entering the secondary market is simply too high.
Ledger is currently upgrading supply chain verification standards and urges hardware makers to collaborate on anti-tampering practices industry-wide.
Action Plan for Wallet Owners
If you purchased a device from CryptoBilis or any third-party reseller, here is what you need to do immediately:
- Do Not Use Unopened Devices: If you bought from CryptoBilis and haven't set it up, keep it turned off.
- Transfer Existing Funds: If you already set up a device from this reseller, transfer your crypto to a new recovery phrase generated on a device bought directly from Ledger.
- Buy Direct: Always purchase security hardware directly from official manufacturer websites whenever possible.
Beware of Follow-Up Scams
High-profile security incidents often attract scammers who target worried users. Fake support accounts may offer to 'verify' your device or 'recover' lost tokens.
Remember: Ledger staff will NEVER call you, send you direct messages on social media, or ask for your 24-word secret recovery phrase.
Never enter your recovery phrase on any website, phone app, or computer screen. Keep your recovery words written on paper or metal, stored safely offline.
Latest blog posts
Crypto Fear and Greed Index Drops to Pre-Rally August Lows
Bitcoin sentiment cools to neutral as macro pressures, high oil prices, and rising bond yields trigger crypto ETF outflows.
|

AI Agents Drive Record Traffic on the XRP Ledger
Autonomous AI software is now the main source of transaction activity on the XRP Ledger, outpacing human retail users through microtransactions.
|
Bitcoin Miners Face $50B Gap in AI Pivot as Lenders Tighten
Bitcoin miners need around $50 billion to build planned AI datacenters, but rising funding costs and lender scrutiny pose challenges for firms like IREN, Riot, and HIVE.
|