Cryptobilis Founder Says Firm Was Sold Before Ledger Exploit
The Cryptobilis Founder Breaks His Silence
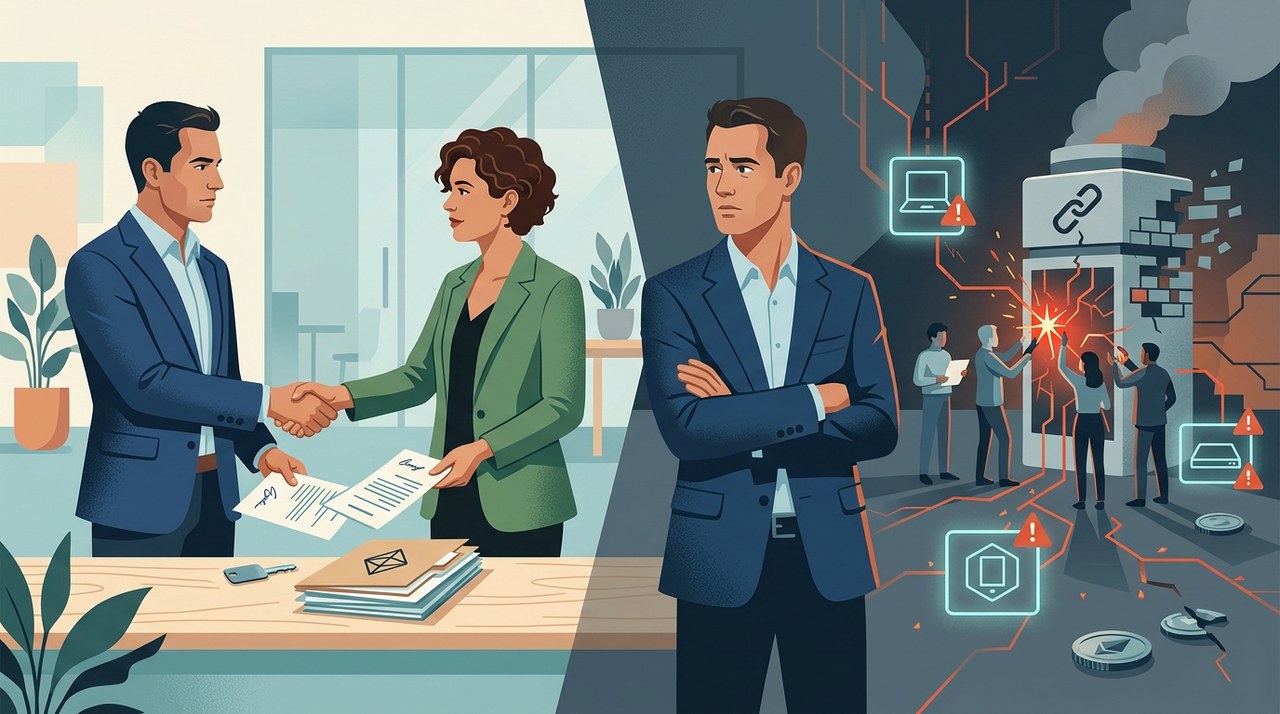
The founder of popular crypto reseller Cryptobilis, Arravind Prabu, has revealed that the company was sold months before a massive security breach occurred. This news comes as crypto holders deal with over $90 million in losses caused by tampered hardware wallets.
Prabu shared this update in a public statement on LinkedIn on October 10. He clearly stated that he and his co-founder stepped down back in March 2026 after selling the business to an undisclosed party.
What Did the Company Sale Involve?
According to Prabu, the ownership change took place early in the year. Once the transaction closed, the original founders completely handed over operational and administrative responsibilities to the new management team.
Prabu emphasized that he no longer had any administrative authority or technical access to the company. He wanted to make it clear that he was not running daily operations when the tampered devices were sold.
- Complete handoff: The original team surrendered administrative and operational duties to the new buyers.
- Zero system access: Prabu claims he lost all access to backend systems, databases, customer order histories, and internal communication channels.
- Advisory role: He only helped the new team briefly in an advisory capacity to coordinate events and ensure a smooth transition.
- Delayed announcement: Prabu explained that non-disclosure contracts prevented him from speaking publicly about the sale until mid-October.
Why Were Customers Kept in the Dark About the Sale?
Many crypto users questioned why the sale of Cryptobilis was kept secret for so long. Prabu explained that strict contractual agreements required him to hold off on public announcements until mid-October.
However, he noted that official suppliers were notified about the management shift. Despite this, several critical questions remain unanswered regarding the physical product inventory.
Specifically, Prabu did not clarify whether existing Ledger hardware stock was included in the handover to the new management. It also remains unclear who had physical access to those hardware devices before each sale.
Ledger Halts Shipments as Investigation Continues
Hardware wallet manufacturer Ledger took immediate action after discovering tampered devices coming from Cryptobilis. The company completely paused all shipments and sales of Ledger devices through the distributor to protect users.
Ledger strongly recommended that anyone who recently bought a wallet through Cryptobilis should not set up or use the device. Setting up a compromised device can expose private keys directly to attackers.
For all active operational matters, technical inquiries, or official statements regarding Cryptobilis, please contact the current lead Person in Charge. - Arravind Prabu
Is the Exploit Bigger Than First Thought?
While Ledger's latest updates point to Cryptobilis as the primary source of compromised units, reports indicate the problem might be broader. Modified devices have reportedly turned up in other regions from different authorized resellers.
Total losses linked to this supply chain attack have already passed $90 million. Security teams across the crypto ecosystem are working continuously to track down compromised units and prevent further theft.
This ongoing issue serves as an important reminder about digital asset security risks. Past performance of digital assets or security systems is not a guarantee of future performance or protection against physical hardware tampering.
How to Keep Your Crypto Wallets Safe
Hardware wallets remain one of the most reliable ways to secure digital assets. However, physical supply chain attacks show that vigilance is necessary from the moment a package arrives.
- Buy direct: Whenever possible, order hardware wallets directly from the official manufacturer rather than third-party resellers.
- Inspect packaging: Check for broken anti-tamper seals, modified wrap, or unusual packaging details before opening.
- Never use pre-set seeds: If a device arrives with a pre-printed recovery phrase, it is compromised. Real wallets always generate seed phrases on-screen during initial setup.
- Verify software checks: Always connect your device to the official application, such as Ledger Live, to verify hardware authenticity before depositing funds.
What Happens Next?
Ledger is continuing its investigation into how these devices were intercepted and modified. In the meantime, Prabu has directed all further technical and operational inquiries to the new management team currently running Cryptobilis.
As the investigation unfolds, the crypto community will be watching closely to see how supply chain verification standards evolve to prevent future physical exploits.
Latest blog posts

Schiff Calls Out Saylor as Strategy's BTC Yield Dips
Gold advocate Peter Schiff claims Michael Saylor's Bitcoin strategy is failing in 2026, pointing to a negative year-to-date Bitcoin yield metric.
|

 +2
Crypto Market Data Signals Cooler Spot Activity Ahead
Weekly data shows $856 million in stablecoins left circulation as spot trading slowed down across major decentralized exchanges.
|

Cardano Sees Record High Network Usage Since 2021
Cardano processed over 1.78 million transactions during Epoch 660, setting a new record driven by community governance voting.
|