
US Judge Clears Brothers in $25M Ethereum MEV Case
US Judge Clears Brothers in Landmark $25 Million EthereumETH-1.58% Case
A high-profile cryptocurrency court case has taken a major turn in federal court. US District Judge Jessica Clarke has cleared two brothers who were accused of orchestrating a $25 million exploit on the Ethereum network.
The ruling came after a mistrial was declared in the trial of Anton Peraire-Bueno and James Peraire-Bueno. In her decisions, Judge Clarke noted that the complex blockchain transactions performed by the brothers did not involve explicit false promises or traditional misrepresentation under federal wire fraud statutes.
Understanding Ethereum MEV and the $25 Million Exploit
To understand why this court decision is so significant, it helps to break down how transactions work on the Ethereum network.
When you send a transaction on Ethereum, it does not get added to the blockchain instantly. Instead, it waits in a public holding area called the mempool. Specialized software bots and block builders scan this pool to organize the order of transactions before they are finalized.
What is MEV (Maximal Extractable Value)?
MEV refers to the maximum value that can be extracted from block production by reordering, inserting, or censoring transactions inside a block. Think of it like someone standing in a busy line at a theme park who pays extra to jump ahead of you because they saw which ride you were heading toward.
In April 2023, the brothers allegedly exploited vulnerabilities within MEV-Boost software relays. Within just 12 seconds, they managed to manipulate pending transactions and divert roughly $25 million worth of crypto assets into their own accounts.
The Legal Defense: Code Execution vs. False Promises
Federal prosecutors had charged the brothers with wire fraud, arguing that they tricked the network relays into releasing private transaction data ahead of time.
However, the defense argued that no deceit or lying occurred in the traditional legal sense. The brothers simply interacted with automated smart contract code according to how the protocol was designed, even if the result was unexpected by the software developers.
Judge Jessica Clarke stated that the transactions did not involve false promises, pointing out the technical distinction between manipulating protocol software mechanics and making deceptive claims to human victims.
Ethics vs. Legality: What the Ruling Did Not Decide
While the judge cleared the brothers on the primary fraud counts following the mistrial, the ruling was carefully framed. Judge Clarke explicitly emphasized that the court did not determine whether the brothers' conduct was ethical.
Furthermore, the ruling did not settle whether their actions might have violated other state laws, civil statutes, or regulatory guidelines outside the scope of federal wire fraud.
- Legal standard: Wire fraud requires proving intentional misrepresentation or false promises, which the judge found lacking in automated code execution.
- Ethical boundaries: Exploiting code vulnerabilities remains heavily debated within the decentralized finance community.
- Future exposure: The decision leaves open potential civil lawsuits or alternative regulatory claims.
What This Precedent Means for Crypto Developers and Traders
This case was closely watched across the crypto ecosystem because it represents one of the first times federal prosecutors attempted to criminalize MEV searcher behavior using traditional fraud laws.
For developers, the case highlights the urgent need for robust smart contract auditing and secure relay designs. For traders, it reinforces the unpredictable nature of decentralized finance environments where advanced trading bots actively scan for extraction opportunities.
As public blockchains continue to evolve, lawmakers and judges are still grappling with how legacy financial regulations apply to automated code. Past performance of digital assets is not indicative of future returns. You can track live network activity and asset parameters via the Bitkub ETH Market.
Latest blog posts


 +2
Ledger Clarifies Web Incident Caused by Third-Party Service
Hardware wallet maker Ledger addressed a web security incident linked to provider Optimizely, confirming user private keys and hardware devices remained safe.
|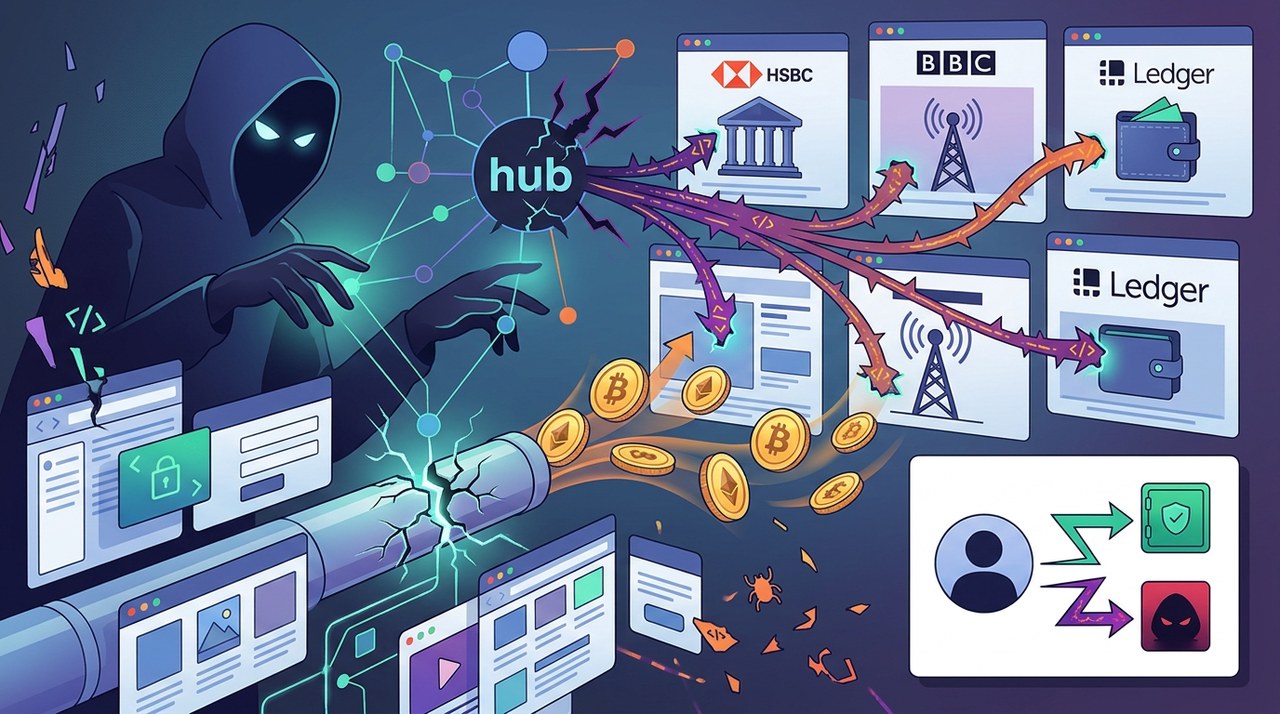

Major Flaw Exposes 178 Websites to Crypto Theft
Hackers used a flaw in Optimizely to place malicious code on 178 websites, including HSBC and Ledger, swapping wallet addresses to steal funds.
|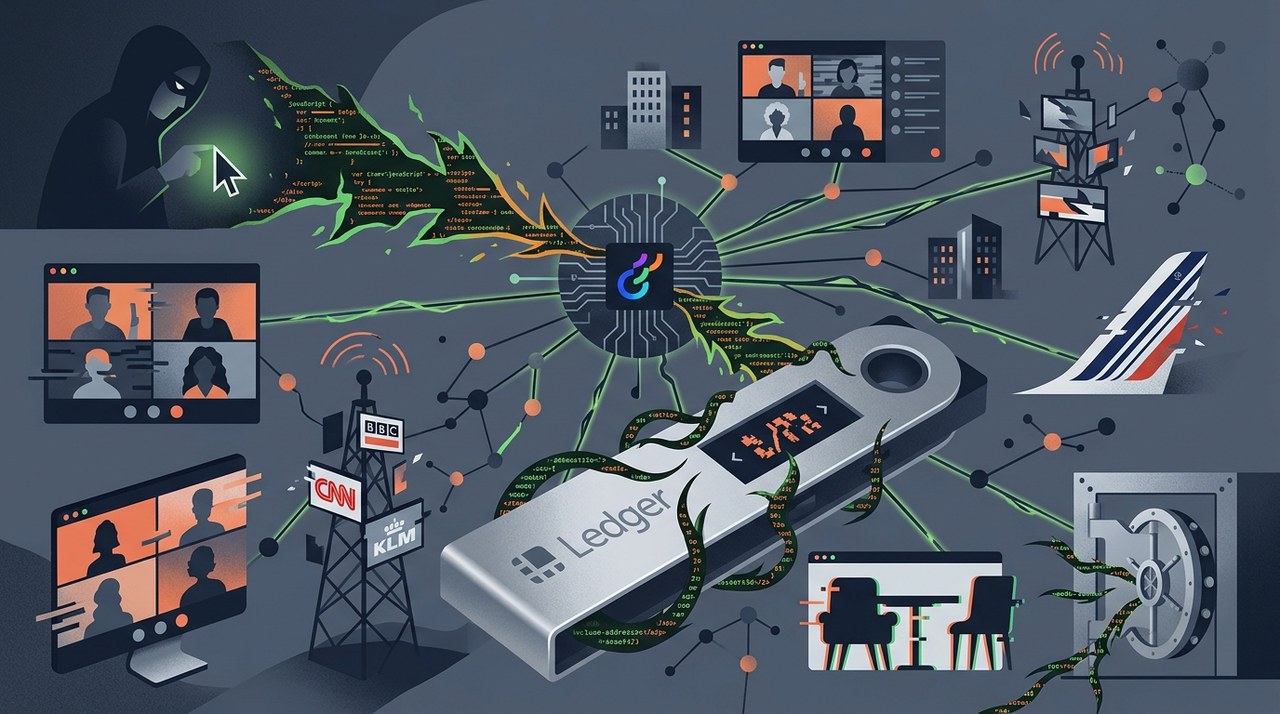
Hackers Target Ledger and 177 Brands in Web Attack
A security breach at web testing platform Optimizely allowed hackers to inject wallet-swapping code across 178 websites, including hardware wallet maker Ledger.