
Lighter Recovers $5M After $10.4M Security Exploit
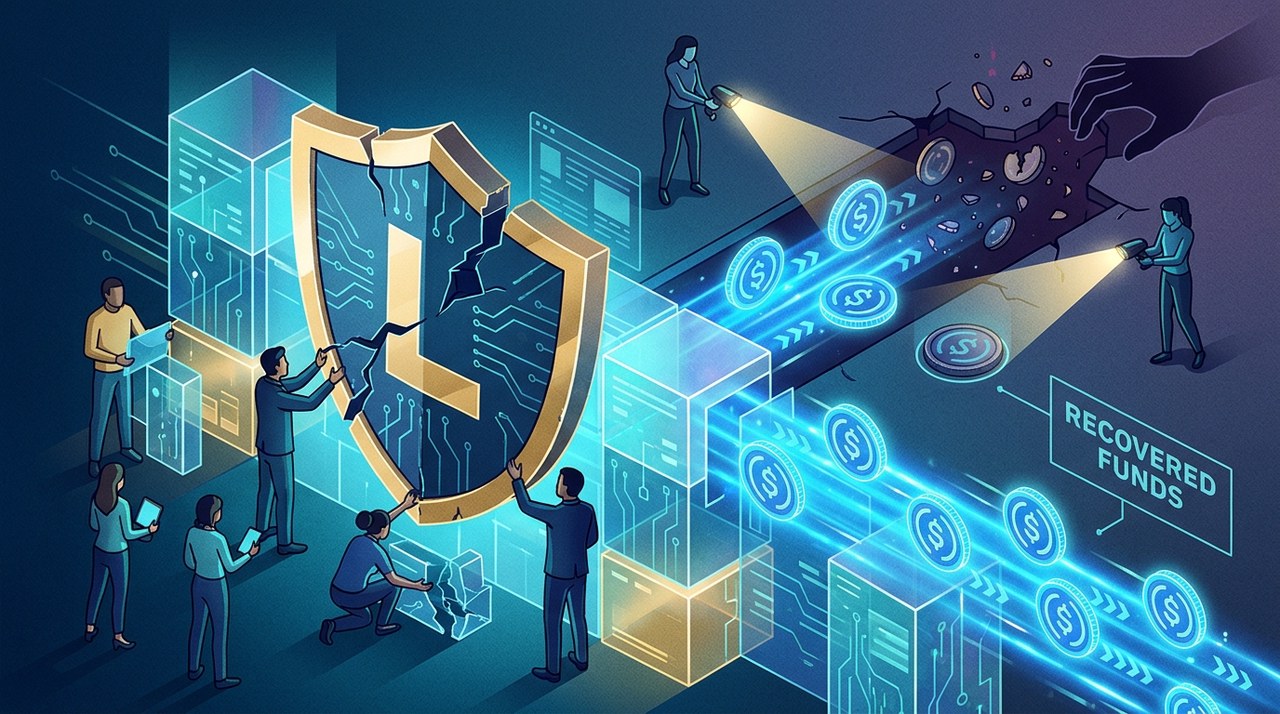
Lighter Restores Withdrawals Following $5 Million USDCUSDC+0.00% Recovery
Decentralized crypto protocol Lighter has officially restored user withdrawals after successfully recovering roughly $5 million in USDC. The recovery follows a recent security incident where attackers moved an estimated $10.4 million from the platform.
Blockchain analysis tools helped trace the unauthorized movement of funds shortly after the breach occurred. The security issue was tied to compromised API keys, which granted unauthorized access to system actions.
Breaking Down the $10.4 Million Incident
Security breaches in decentralized finance can happen for several reasons. Sometimes smart contracts contain bugs within their code. In other instances, vulnerabilities arise from administrative access points or backend infrastructure.
In the case of Lighter, blockchain analysts monitored on-chain activity as $10.4 million moved out of protocol-managed wallets. The sudden movement of funds triggered alerts across the crypto security ecosystem.
Understanding the Role of API Keys
Application Programming Interfaces, commonly referred to as API keys, act like digital access cards between different software systems. They allow automated programs, trading software, and administrative tools to communicate and run instructions automatically without requiring manual logins every time.
When an API key becomes compromised, an unauthorized third party can issue commands as if they were an authorized operator. If that key holds permissions to move funds or interact with system funds, attackers can exploit those access rights to transfer digital assets out of the protocol.
An Everyday Analogy: The Master Key
Think of an API key like a digital spare key to an office building. Imagine a company puts a spare key inside a lockbox so the maintenance team can enter after business hours.
If an unauthorized person finds the code to that lockbox, they do not need to break windows or pick locks. They can simply open the door using the spare key and walk inside. That is essentially what happens when an attacker gets access to compromised API keys in a crypto environment.
The Recovery Process and Reopening Withdrawals
Following the detection of the unauthorized transfers, security teams and blockchain analysts worked to trace the destination of the funds. Their tracking efforts resulted in the recovery of approximately $5 million in USDC.
USDC is a popular dollar-backed stablecoin issued by Circle. Because blockchain transactions are transparent, security analysts can track fund movements across wallet addresses in real time.
Once the team secured the $5 million in recovered USDC and contained the underlying security issue, Lighter officially restored withdrawal functionality for its users. Reopening withdrawals allows customers to manage their account balances again.
Summary of Key Facts Regarding the Lighter Security Incident
Here is a quick overview of the key details reported during this incident:
- Total Funds Moved: Blockchain analysts traced $10.4 million in unauthorized fund movements during the exploit.
- Cause of Breach: The exploit was linked to compromised API keys.
- Funds Recovered: Approximately $5 million in USDC was successfully recovered.
- Platform Status: Withdrawals have been restored for users after security checks.
Why API Key Management Is Essential for Crypto Security
This incident highlights the importance of robust security practices across all digital asset platforms. While smart contract auditing is essential, operational security around administrative keys is equally critical.
Developers and automated systems rely heavily on API keys to handle tasks like automated trading and price monitoring. If secret keys are exposed or improperly stored, unauthorized parties can scan for them and misuse their privileges.
Best Practices for Handling API Security
Both platform developers and individual users who utilize automated trading tools can follow key practices to minimize risks:
- Restrict IP Access: Restrict API keys to specific, trusted IP addresses so leaked keys cannot be used from unknown locations.
- Limit Key Permissions: Never enable withdrawal permissions on API keys unless absolutely necessary. Trading keys should generally be limited to placing or canceling orders.
- Rotate Keys Regularly: Periodically replacing old API keys with new ones reduces the window of opportunity for attackers.
- Store Credentials Privately: Keep API secret keys stored in secure environment variables or dedicated secret management services rather than plain text files.
What This Means for Users and the Broader Market
Security incidents serve as important reminders of the risks associated with digital asset ecosystems. However, the quick recovery of $5 million in USDC demonstrates how public ledger tracking can assist incident response teams in mitigating losses.
For traders and liquidity providers, monitoring official updates and understanding security measures are important elements of managing crypto assets. Digital asset markets carry risk due to price volatility and potential security vulnerabilities, making careful risk management essential.
Past performance of digital assets or security outcomes does not guarantee future results. Staying informed and reviewing protocol disclosures helps users make more educated choices when navigating crypto platforms.
Latest blog posts

Bitcoin Volume Surges to Highest Level Since February
Bitcoin daily trading volume hit multi-month highs following a drop to $55,100, triggering $562 million in liquidations as prices bounced back.
|

 +1
Anthropic IPO, Saylor Strategy, and Quantum Bitcoin Security
A friendly weekly recap covering MicroStrategy plans, Anthropic IPO impacts on Bitcoin ETFs, Hong Kong regulatory alerts, and quantum security research.
|
Fed Rate Hikes Could Extend Beyond December as Inflation Stays High
Federal Reserve Governor Lisa Cook signals that interest rates might stay higher for longer, impacting both traditional stocks and cryptocurrency markets.
|