
Keystone Scraps 18,835 Crypto Wallets After Key Leak
What Happened at Keystone?
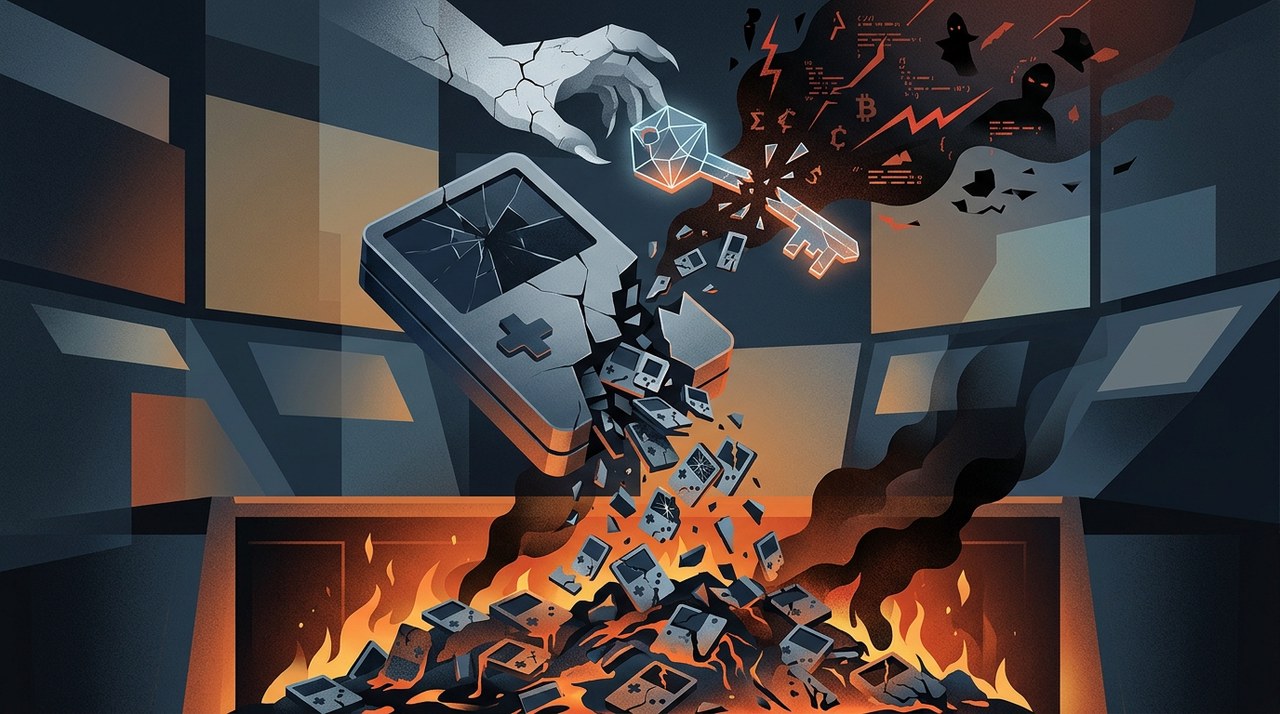
Imagine locking your savings in a high-tech vault, only to find out a burglar got a copy of the master key builder. That is essentially what happened to BitcoinBTC+0.72% hardware wallet maker Keystone.
On October 20, Keystone detected a major security breach. Attackers managed to steal a permanent factory key used by the company to confirm that a device is genuine.
To protect crypto users, Keystone announced on Monday that it will destroy 18,835 unsold hardware wallets. The company has also paused all pending shipments from its website.
Understanding the Web Auth Key Threat
What makes a hardware wallet so special? It keeps your secret codes completely offline, far away from online hackers and malware.
When you set up a Keystone wallet, a special code checks if the hardware is real. Keystone calls this the Web Auth key.
Think of this key like a unique wax seal stamped on every device at the factory. When you plug in your wallet, Keystone's website checks that seal.
Because the attacker stole this master seal code, they could build fake wallets that pass Keystone's official verification test.
If it is exposed, an attacker could use it to produce counterfeit devices that pass authentication checks. These devices could then be sold or shipped to customers, who might unknowingly use them as genuine products, potentially resulting in asset theft.
A scammer could sell a fake device to an unsuspecting buyer. When the user loads real funds onto it, the criminal could steal everything.
Since the Web Auth key is written directly into the chip hardware, it cannot be erased or updated. That is why Keystone must destroy all 18,835 inventory units.
Are Existing Keystone Devices Safe?
If you already own a Keystone wallet, you might be asking: is my crypto in danger?
Here is the good news. Keystone confirmed that secret recovery phrases and private keys were not involved or exposed in this attack. Your funds remain secure on the blockchain.
Additionally, devices delivered before October 20 are completely unaffected by the factory key leak.
The company has paused all current web store orders. Future orders will switch to a preorder system until new devices with fresh factory keys are produced.
The Customer Data Breach and Shopify Glitch
Unfortunately, the factory authentication key was not the only thing exposed during the security incident.
Keystone first revealed on Saturday that customer shipping information was accessed by a third party. On Monday, they confirmed the full scale of the leak.
The breach exposed 25,964 buyer records from Keystone's Shopify store between 2024 and 2026.
- Exposed details include full customer names, contact phone numbers, and physical shipping addresses.
- Order details and purchase history information were also accessed by the attacker.
- Purchases made through Amazon or other third-party retail channels were not affected.
In total, 51,083 buyer records were involved in the system. Luckily, 25,119 records had already been erased prior to the attack.
Keystone admitted that their automated data deletion tool failed to work properly. The company's policy was to erase buyer records after 180 days.
Some erasure tasks failed, and we did not detect and address these failures in time, resulting in certain personal information being retained beyond the permitted period. We failed to fulfill our commitment to erase customer data on time, and we accept responsibility for this failure.
To prevent future issues, Keystone reduced its data retention period from 180 days to 90 days. On October 24, they asked Shopify to wipe all overdue data, a process expected to finish by November 3.
Why Leaked Addresses Are a Major Risk
In the crypto world, privacy is closely tied to physical safety. Leaked home addresses can expose crypto owners to targeted threats.
Security analysts warn of physical threats often referred to as wrench attacks. Criminals use coercion or force to compel victims to transfer their crypto holdings.
Blockchain analytics company Chainalysis counted 46 violent physical attacks in the first half of 2026 alone, with victims losing over $30 million.
Keystone is not the only hardware wallet manufacturer to experience customer data breaches in recent years.
- Ledger suffered a major customer leak in 2020 that exposed roughly 292,000 user details.
- Trezor disclosed a customer data breach in August impacting 13,689 customers.
- SafePal reported a data breach in August that affected approximately 39,798 user records.
Beware of Follow-Up Phishing Scams
After data breaches occur, scammers frequently target victims with sophisticated phishing messages and trick offers.
Bad actors may pretend to offer asset migration, wallet verification, or fake investigation assistance.
We will not ask you to return your device. Anyone contacting you under the pretext of a 'recall' and asking you to ship your device to them should be treated as a scammer.
Never enter your 12 or 24-word seed phrase on any website or share it with anyone. Hardware wallet teams will never ask for your private keys.
Regulatory Actions and Market Note
Keystone stated that it has formally submitted incident reports to data privacy authorities in the European Union, the United Kingdom, and other jurisdictions.
During this event, Bitcoin traded around $80,644, seeing typical daily fluctuations between $79,416 and $80,573.
Past performance of digital assets is not an guarantee of future performance. Always exercise caution and follow strong security practices when managing crypto hardware.
Latest blog posts
Brazil Supreme Court Sets Nov 3 Hearing on Betting Ban
Brazil's Supreme Court has scheduled a public hearing for November 3 to discuss the country's online betting ban after 85 operator licenses expired.
Poll: Americans Want Candidates Supporting US Fintech
A September survey reveals that most US voters favor political candidates who support domestic financial technology and digital asset policies.

Circle Brings USDC Settlement to Colombia Banking System
Circle has partnered with ACI Worldwide to test USDC stablecoin settlements within Colombia's traditional Bre-B instant payments network.
|