
Hackers Target 178 Major Websites in Crypto Address Attack
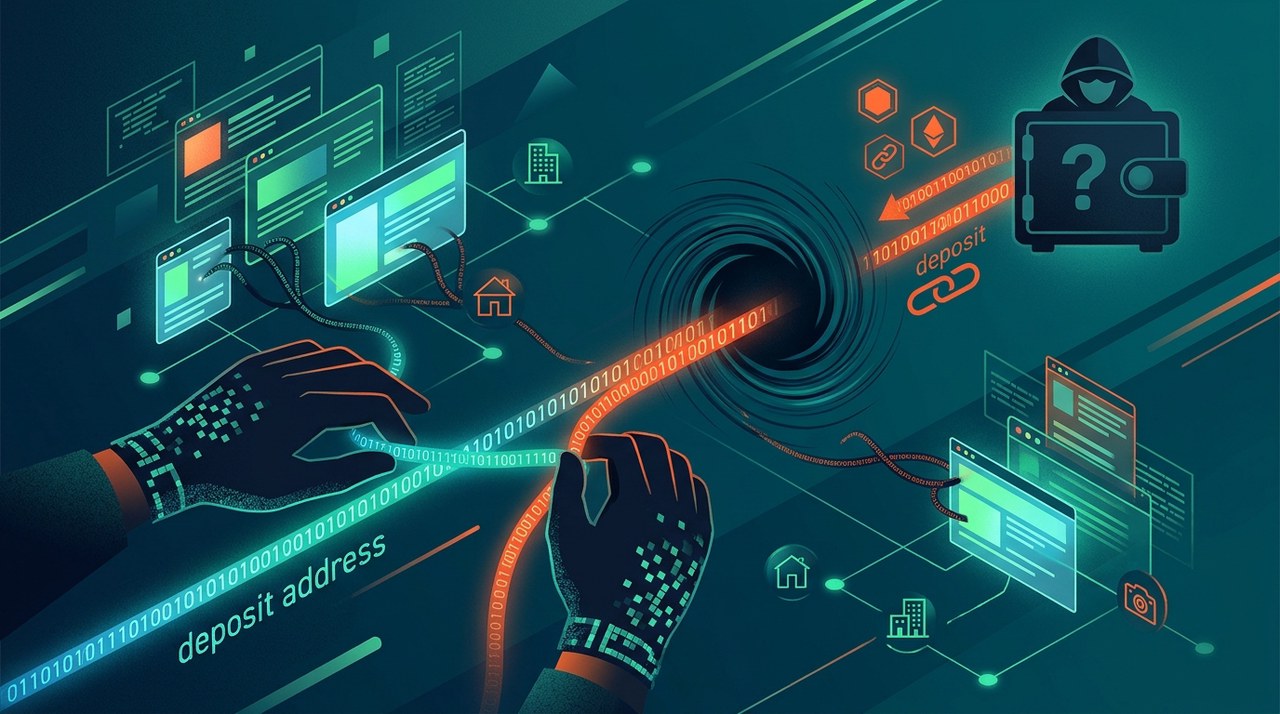
A Sneaky Malware Attack Hits 178 Major Websites
Cybersecurity researchers at Report URI recently discovered a widespread supply chain attack that injected crypto-stealing malware into 178 prominent websites. Major brands including hardware wallet manufacturer Ledger, global banking institution HSBC, and video communications platform Zoom were among the targets.
Unlike a direct exchange hack where security perimeters are breached, this attack compromised third-party web software used by trusted brand websites. As a result, crypto users who copied deposit addresses from these infected pages were at risk of sending their funds straight to an attacker's digital wallet.
How the Optimizely Attack Unfolded
The attack stemmed from Optimizely Web, a popular analytics and testing tool that companies use to experiment with different webpage layouts. Attackers managed to plant unauthorized code directly inside customer projects hosted on the platform.
Because Optimizely's own distribution network delivered this script to site visitors, the malicious code executed automatically whenever users loaded the affected web pages.
Who Was Impacted?
The breach impacted organizations across multiple industries, with banking and financial services being the most affected sector, counting 32 compromised organizations. Another six organizations came directly from the crypto and trading space.
Some of the notable names identified in the security report include:
- Ledger (Crypto hardware wallet manufacturer)
- HSBC (Global banking institution)
- Zoom (Video conferencing software provider)
- CNN & BBC (International news networks)
- Salesforce (Enterprise cloud platform)
- IKEA (Global retail brand)
- Equifax (Credit reporting agency)
- Air France-KLM (Major airline alliance)
Malware Features and Financial Losses
The main goal of the injected code was to monitor web pages for cryptocurrency addresses and swap them with addresses controlled by the attacker. If a user attempted to copy a deposit address from an infected page, the clipboard or page text yielded the hacker's address instead.
As the attack progressed, updated versions of the malware expanded their capabilities. Security researchers noted that later iterations included credit card skimmers to intercept payment details, alongside exploit kits aimed at vulnerable iPhones and iPads.
Report URI estimates that the attacker managed to steal approximately $7,040 in cryptocurrency within a nine-hour window before the attack vector was neutralized.
Optimizely confirmed that it addressed the underlying vulnerability, removed the injected code, and secured all affected customer accounts. Nevertheless, this incident echoes the Bitwarden supply chain breach from earlier this year, where attackers similarly targeted third-party code to compromise crypto wallet keys.
Google Warns That AI Tools Are Accelerating Exploits
While there is no direct evidence linking the Optimizely incident to artificial intelligence, security researchers highlight that automated cyberCYBER-1.89% threats are growing rapidly across the industry.
Google's Threat Intelligence Group (GTIG) published a report detailing how threat actors are now leveraging AI frameworks to analyze software security patches. By comparing software code before and after a security patch is released, tools like an AI framework named exploit_agent can automatically reverse-engineer patches into working exploits without human intervention.
GTIG previously identified the first AI-built zero-day exploit in May, pointing out that AI is dramatically reducing the time between a patch release and a fully weaponized attack.
For the most part, attackers aren’t using new groundbreaking methods to break into systems — they are still going after known, unfixed issues, just with much greater speed and scale.
John Hultquist, Chief Analyst at Google Threat Intelligence Group, emphasized that software vulnerabilities remain the primary target, but automated tools now allow hackers to strike faster than ever.
Social Engineering Attacks Target Crypto Organizations
Alongside automated software exploits, human-targeted attacks remain a primary vector for crypto threats. GTIG highlighted an active campaign by a suspected North Korean hacking group posing as corporate recruiters.
The group targeted employees at crypto firms across North America and Europe, using fake job interviews and recruitment tasks to deliver malware directly into corporate networks. A similar social engineering tactic was tied to a security incident involving Binance.
More than 100 technology companies, including leading AI firms OpenAI and Anthropic, have previously cautioned that AI-driven cyber threats would scale rapidly within months.
Protecting Wallet Operations in a Supply Chain Threat Environment
These security incidents demonstrate that attackers increasingly compromise third-party software dependencies rather than attacking underlying blockchain networks directly. When relying on web interfaces, routine copy-and-paste actions can become potential single points of failure.
Security experts recommend verifying wallet addresses character-by-character on hardware wallet screens or secondary devices before confirming transactions, sending small test transactions when transferring funds, and maintaining updated security software on desktop and mobile operating systems.
Latest blog posts

Grayscale Views Market Dip as Bitcoin Hits $64,000
Grayscale Head of Research Zach Pandl highlights strong underlying crypto demand through institutional stablecoin adoption, even as Bitcoin pulls back to $64,000.
|
Bitcoin Could Slide into $50k Range as Risks Mount
Market maker Wintermute warns Bitcoin could retest the $50,000s due to ETF outflows, weak spot demand, and Fed rate hike concerns.
|
Could an AI Bubble Burst Impact Bitcoin's 2028 Halving?
Former SEC Chair Gary Gensler warns that an AI bubble could trigger an economic slowdown before late 2028, coinciding with Bitcoin's next block reward reduction.
|