
Engineer Gets 32 Months for Bitcoin Ransom Scheme
An Inside Job Gone Wrong
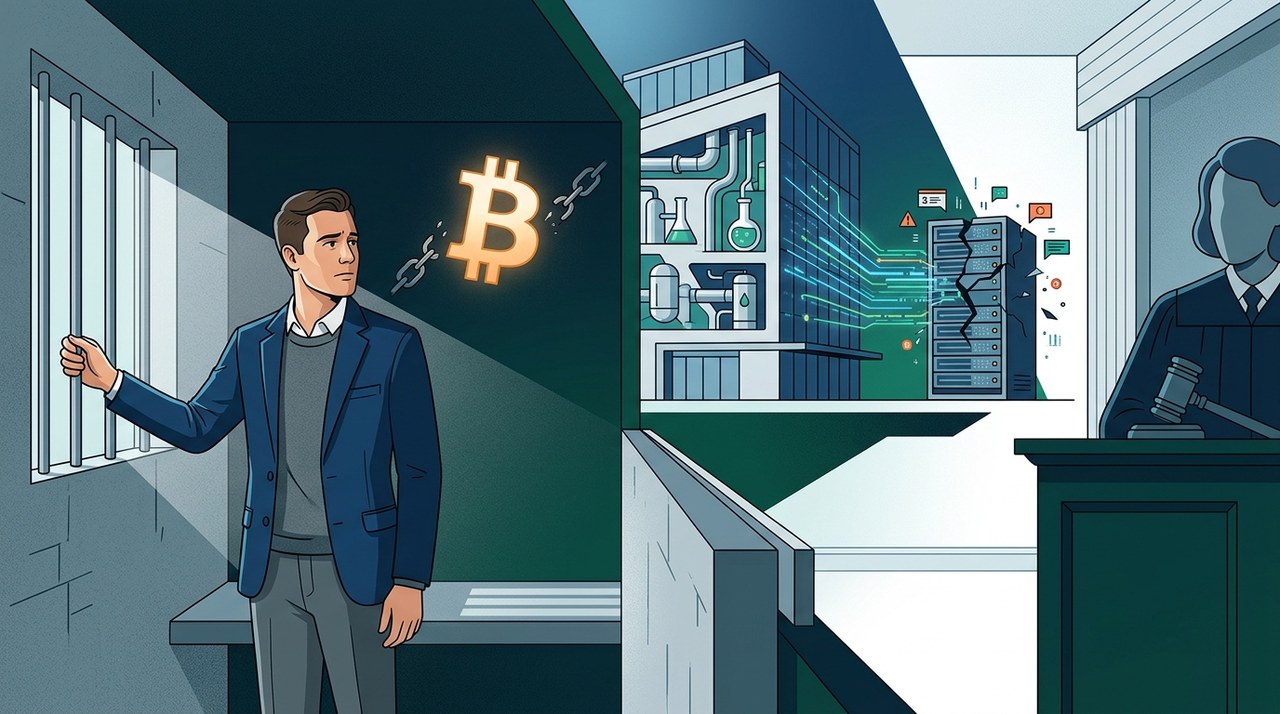
Imagine being the top IT expert at a major company and using your skills to turn against your employer. That is exactly what happened in a high-profile cybercrime case in New Jersey.
Daniel Rhyne, a 59-year-old former core infrastructure engineer from Kansas City, Missouri, was sentenced to 32 months in prison on September 28. U.S. District Judge Michael A. Shipp handed down the ruling in Trenton, New Jersey.
Back in April, Rhyne pleaded guilty to two federal charges. These included extortion related to threatening a protected computer and intentionally causing damage to a protected computer.
How the Cyberattack Unfolded
Rhyne worked as the primary virtual machine expert for an industrial company headquartered in Somerset County, New Jersey. The firm supplies services to vital sectors like biopharmaceuticals, oil, and gas.
The incident started around 4:00 PM on November 25, 2023. System administrators suddenly began getting password reset alerts for hundreds of accounts.
They quickly realized that every other domain administrator account on the network had been erased.
Just 44 minutes later, workers received an email with the subject line "Your Network Has Been Penetrated."
The email stated that IT admins were locked out and backups were destroyed. The attacker demanded 20 BitcoinBTC-3.26%—worth about $750,000 at the time, or roughly €700,000—by December 2.
If the company refused to pay, the ransom note threatened to shut down 40 servers every day for 10 days.
The Secret Machine and 'The Fr0zen Crew!' Password
Federal investigators quickly uncovered a hidden, unauthorized virtual machine created on the company network on November 9, 2023.
The creator used the password "The Fr0zen Crew!" for this hidden system.
Investigators found that exact same password applied to an admin account, 301 user accounts, and the email address that sent the ransom note.
On the morning of the attack, someone used a remote desktop session from that hidden machine to set up destructive scheduled tasks.
These tasks were designed to delete 13 administrator accounts, change passwords across 254 servers and 3,284 workstations, and force server shutdowns starting December 3.
How the FBI Tracked Down the Engineer
The FBI connected the secret virtual machine straight to Rhyne's official company laptop through several key clues:
- Web browsing on Rhyne's company laptop stopped whenever browsing activity started on the hidden machine.
- Building keycard logs showed Rhyne entering headquarters just minutes before his account logged in.
- On the attack date, his laptop accessed the network from an IP address registered to his home in Warren County, New Jersey.
- Web history showed searches for 'how to clear all windows logs from command line' and 'how to remotely shutdown a computer using cmd' days before the incident.
Final Sentences and Legal Outcomes
Rhyne was originally charged with wire fraud too, but that charge was dropped as part of his plea agreement.
He faced up to 5 years for the extortion count and up to 10 years for damaging protected computers.
In the end, Judge Shipp sentenced Rhyne to 32 months in federal prison.
Past performance of digital assets or historical prices mentioned in news events are for contextual purposes only and do not guarantee future market results.
Latest blog posts
Europol Warns Quantum Attacks Threaten Crypto Wallets
Europol warns quantum computing could break crypto wallet encryption and urges developers to adopt post-quantum security early.
|
Tesla Shares Slip Early Wednesday Despite Q3 Delivery Beat
Tesla stock experienced a slight pullback despite beating third-quarter delivery estimates, as investor attention shifted toward regulatory developments in Europe.
BlackRock Discovers Major Disconnect Between Women and Financial Advisors
A new BlackRock study reveals that financial advisors frequently misjudge how wealthy women earn their money and what they want from financial advice.