
Electrum Fixes Flaw Used to Steal Bitcoin Via Fee Bumps
What Happened to the Electrum BitcoinBTC+0.08% Wallet?
If you use the Electrum Bitcoin wallet, there is an important security update you need to know about. Developers recently released version 4.8.3 to fix a high-severity security flaw that allowed attackers to steal user funds.
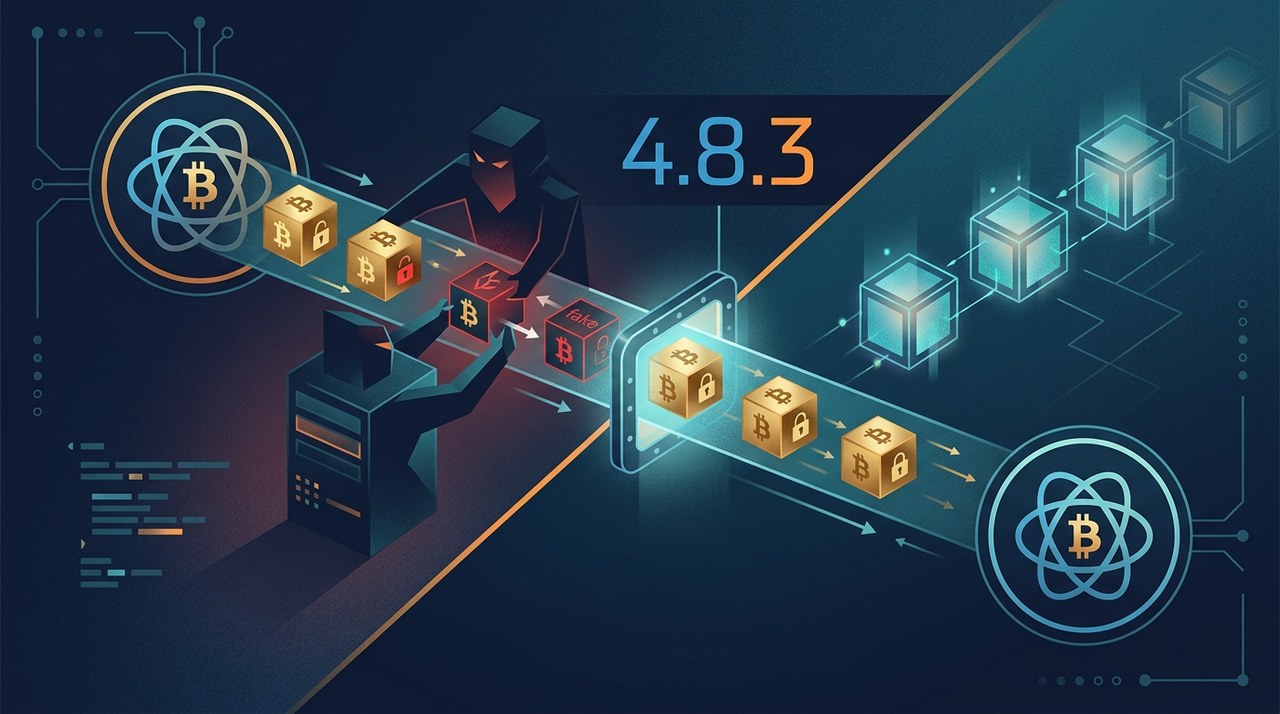
The vulnerability affected every version of Electrum released before version 4.8.3. It allowed rogue servers to quietly manipulate unconfirmed Bitcoin transactions right under the owner's nose.
How the Attack Sneaked Past Wallet Security
Electrum is a popular lightweight wallet. To work quickly, it relies on external servers to fetch transaction history and broadcast payments to the Bitcoin network.
While older Electrum versions verified confirmed transactions, they accepted unconfirmed transactions without checking their cryptographic signatures. Malicious servers exploited this exact gap.
A compromised server could intercept your payment before it hit the blockchain. It would then swap your payment with a fake transaction sending your coins to an attacker instead.
The Fee Bump Trap: How Victims Were Tricked
To make matters worse, the fake transaction appeared inside the wallet as an ordinary pending payment. Attackers even generated destination addresses whose final four characters matched the real address.
The trap was sprung when users tried to speed up their transaction using the Replace-By-Fee feature. When trying to increase the transaction fee, the user unknowingly signed the hacker's fraudulent payment.
Once signed by the user, the stolen transaction became valid and was permanently processed on the Bitcoin blockchain.
Real Victims and the Security Fix
This attack was not just theoretical. On October 11, a user named dannydeezy reported seeing transaction substitutions. Then on October 18, another user named Raju-K12 confirmed losing funds after approving a fee increase.
Electrum developers patched the loophole in commit 90fe308. The new version 4.8.3 automatically checks signatures on unconfirmed transactions. If a signature is invalid, Electrum rejects it immediately.
How to Keep Your Crypto Safe
If you use Electrum, you should update your wallet software immediately. Here are the core security actions you should take right away:
- Download updates exclusively from the official site at electrum.org.
- Verify the cryptographic signature of the downloaded installer file.
- Carefully inspect recipient addresses and amounts before signing any fee adjustments.
- Consider connecting exclusively to a private, self-hosted Electrum server.
Users running their own private servers were not exposed to this server-side attack. However, public server users must update to stay protected.
Wider Crypto Security Context
This incident shows how clever attackers can exploit subtle software flaws. Even wallets built to safeguard private keys can be manipulated into requesting real signatures for fake payments.
In related security news, hardware wallet maker Keystone also disclosed a recent website breach that exposed customer shipping details and names.
Remember that digital assets like Bitcoin carry market risk and high volatility, trading near $80,855 at the time of publication. Past performance of digital assets does not guarantee future results. You can view market details on Bitkub Market.
Latest blog posts


Ripple & Cryptescrow Partner to Ease Real Estate Deals
Ripple has partnered with real estate settlement provider Cryptescrow to allow cryptocurrency holders to purchase high-value property using converted U.S. dollars.
|

 +1
AI Voice Models Guess Bitcoin Price: Can You Trust Them?
A Bitcoin.com experiment tested voice and text AI models predicting Bitcoin's price, revealing surprising gaps between confidence and actual financial analysis.
|

Dogecoin Contributor Outlines Steps for DOGE Growth
Dogecoin contributor Mishaboar shared key recommendations for commercial ventures to support core development and strengthen the network ecosystem.
|