

Bitcoin Core Updates Security Rules as AI Uncovers Code Flaws
Why Bitcoin Core Is Changing Its Security Policy
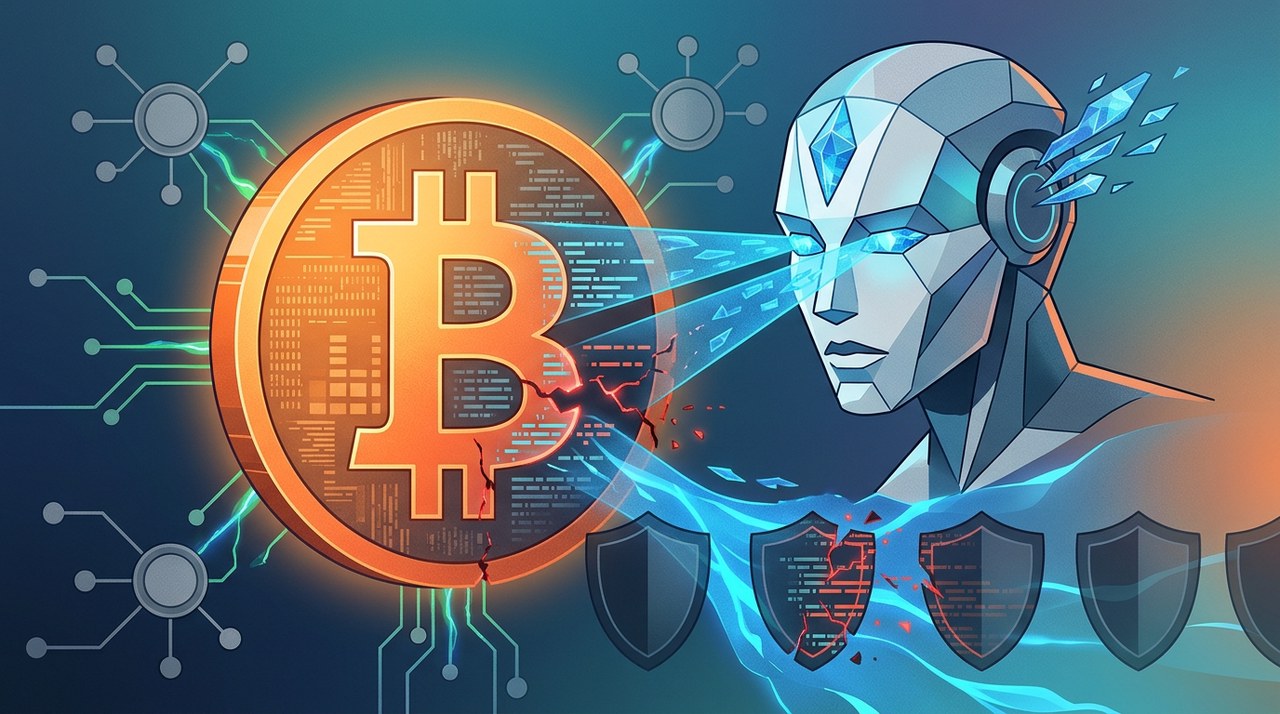
Bitcoin Core developers have officially merged a major policy change to how software security flaws are handled. For years, the project kept security bugs hidden under strict embargoes to give users time to update their software. Now, artificial intelligence is changing how code is analyzed.
Artificial intelligence tools can now spot hidden code vulnerabilities in seconds. Because an AI model can rediscover a hidden bug with a simple prompt, keeping bugs secret for months no longer protects users.
How the Old Security Embargoes Worked
In the past, Bitcoin Core classified security bugs based on severity levels. Minor flaws were disclosed two weeks after the next major software release shipped. Medium and high-severity flaws were kept under strict non-disclosure embargoes.
These embargoes often lasted until two weeks after the last affected software version reached its end of life. In practice, this meant a bug fix could stay secret for up to a year.
The goal of the old policy was to protect the network. Developers wanted to patch issues quietly so node operators—the computers that verify and relay bitcoin transactions—had ample time to upgrade before attackers learned about the hole.
Why AI Broke the Old System
The traditional embargo system relied on a key assumption: finding software bugs required specialized human skills and extensive time. The widespread release of AI tools like Large Language Models (LLMs) completely dismantled that assumption.
Antoine Poinsot, a developer at Chaincode Labs who authored the policy proposal, explained that AI drastically lowers the technical barrier to finding vulnerabilities. Attackers can use AI models to inspect code changes or prompt an LLM to identify covert flaws.
We recently experienced an increase in the number of reports for security vulnerabilities that can be easily (re-)discovered. This is largely due to LLMs drastically reducing the bar to find certain classes of issues or identify covert fixes.
How the New Fast-Patch Policy Works
Under the new policy, developers will evaluate incoming security reports during triage. If a vulnerability can be easily found with a simple prompt to an LLM, Core will no longer hold back the details.
Instead, developers will backport the fix to all supported software versions and release a point update as soon as possible. Each fast-tracked release will be accompanied by a public security advisory explaining the vulnerability.
Poinsot acknowledged that this approach carries a trade-off. Fast releases will have less time for testing and review before reaching users. However, developers concluded that holding onto secrets that AI can regenerate presents a far greater risk to the network.
Debate Among Security Researchers
The policy change sparked debate within the bitcoin security community. Antoine Riard, a longtime bitcoin security researcher, suggested that Core should retain the option to release quiet fixes without public advisories on a case-by-case basis.
Poinsot rejected that approach, arguing that vague security alerts without full technical context could cause unnecessary panic and force users into rushed software updates.
Real-World Proof: The Summer AI Bug Invasion
Recent events highlight why Bitcoin Core moved quickly to update its rules. In late July, a volunteer group called the Bitcoin Red Team, consisting of 16 developers, ran AI models across 390 bitcoin projects over approximately 24 hours.
The AI tools identified 4,962 potential issues, including 85 critical security vulnerabilities.
- BTCPay Server: A flaw reported privately by the red team was exploited on live merchant servers within days, draining Lightning Network nodes used for everyday payments.
- Core Lightning: Developers advised node operators to disconnect after AI-generated bug reports sent to their team turned out to be real vulnerabilities.
- Coldcard Hardware Wallets: A vulnerability active since 2021 allowed attackers to steal 594 BTCBTC+0.00% in 25 minutes on July 30. Total losses across four separate sweeps reached nearly $114 million. Coldcard noted that AI assisted in finding additional bugs while preparing the fix.
Broader Ecosystem Impact
Security adjustments driven by AI are occurring across the wider digital asset ecosystem. For instance, EthereumETH+0.07% developers recently delayed testing for their planned Glamsterdam upgrade after security researchers identified risks to existing smart contracts.
Market activity also reflects ongoing volatility across major cryptocurrencies, with Bitcoin hovering near $81,000 to $81,700. Investors should keep in mind that past performance of digital assets is not an indication of future results.
Looking Ahead
Although no bugs have been flagged under Bitcoin Core's new policy yet, open-source developers recognize that AI has permanently altered software maintenance. Moving forward, quick public disclosure and fast patching will serve as the primary defense against automated exploit discovery.
Latest blog posts
 +2
XRP and Zcash Gain Millions as Bitcoin ETFs See Outflows
Institutional capital shifted into XRP and Zcash while Bitcoin spot ETFs recorded $635 million in daily outflows amid a broader market dip.
|
Interpol Seizes $105M in African Cybercrime Crackdown
Interpol and police across 21 African nations shut down illegal crypto mines and recovered over $105 million in stolen funds.

 +2
Bitcoin Holds $81,600 as Open Interest Hits $140 Billion
Bitcoin is trading near $81,600 as futures open interest hits $140 billion, pointing to key resistance levels at $87,500 and support at $80,000.
|