Major JavaScript Hack Hits Optimizely: Zoom, Ledger Affected
A Major Web Exploit Involving Third-Party Scripts
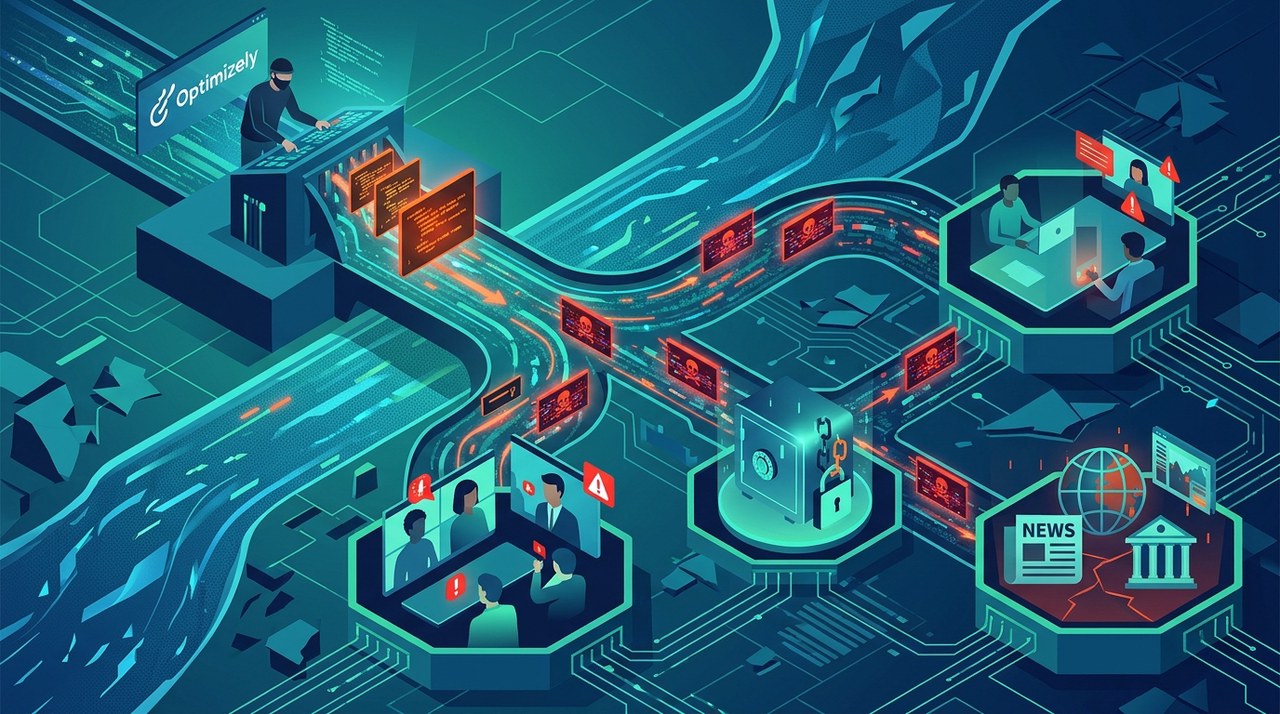
Imagine buying water from your favorite store every day. One morning, someone tampers with the central water plant upstream.
That is essentially what happened across the internet recently. A massive supply-chain attack targeted Optimizely, a popular digital experience platform.
The attackers injected malicious JavaScript code onto mainstream websites. Global names like Zoom, CNN, HSBC, and hardware wallet maker Ledger were among those affected.
What Is Optimizely and Why Do Websites Use It?
To understand this attack, it helps to understand how modern websites work. Big companies rarely build every feature from scratch.
Instead, they plug in third-party services to handle specific tasks. Optimizely provides tools for A/B testing and website optimization.
A/B testing means showing visitors different versions of a webpage. For example, half of visitors might see a green button, while the rest see blue.
Companies use this data to see which version performs better. To run these tests, websites paste a small piece of code called a script snippet into their pages.
When the platform serving those snippets gets compromised, every site loading that script can end up running bad code automatically.
How the Security Flaw Was Discovered
On November 16, security monitoring group Report URI spotted something alarming while crawling web data.
Out of 1,611 Optimizely code snippets scanned by Report URI, 188 contained rogue JavaScript. Researchers suspect the actual number across the web was higher.
At least 178 different organizations had these malicious snippets running on their live web pages.
Cybersecurity news outlet BleepingComputer confirmed that the malicious script loaded on several high-traffic domains.
Which Major Websites Were Targeted?
The list of impacted websites includes major international institutions and media brands:
- Zoom: The video conference tool used by millions daily.
- Media Giants: CNN, BBC, Fox News, and Peacock.
- Financial Institutions: HSBC and credit reporting firm Equifax.
- Enterprise Tools: Salesforce and GitLab.
- Retail and Travel Brands: IKEA and Air France-KLM.
- Crypto Industry: Hardware wallet creator Ledger.
The inclusion of Ledger made this breach especially concerning for cryptocurrency holders who visit the site for updates or support.
What Did the Malicious Script Actually Do?
The hacker's payload was not just a simple bug. It was a suite of tools designed to steal data and financial assets.
1. Swapping Crypto Wallet Addresses
The primary goal of the script was to intercept cryptocurrency transactions by swapping wallet addresses on the page.
If a user tried to copy a deposit address from an affected site, the script replaced it with the attacker's wallet address.
2. Credit Card Skimming
Later on the same day, the attackers updated the script with a card skimmer component.
This skimmer captured credit card details typed into checkout fields before sending them to external servers.
3. Capturing Screenshots and Exploiting Devices
The script could secretly take screenshots of pages the user was viewing, capturing sensitive onscreen info.
It also loaded a hidden iframe designed to execute an iOS exploit chain against visitors using older iPhones.
Financial Losses and Optimizely's Response
According to tracking by Report URI, the attacker's wallet addresses received roughly $7,040 within the first nine hours.
While $7,040 seems relatively small given the massive web traffic of the affected sites, total losses from credit card skimming remain unknown.
Optimizely confirmed that an unauthorized party exploited a vulnerability in its Web Experimentation platform to inject code into customer projects.
The company moved to fix the vulnerability, though the exact technical mechanism of the flaw remains under investigation.
What Does This Exploit Mean for the Crypto Space?
Supply-chain attacks are a growing risk for cryptocurrency platforms and everyday users.
Many Web3 applications rely heavily on traditional Web2 infrastructure, external APIs, and analytics tools.
If a third-party analytics script can alter webpage content, even a secure blockchain backend cannot protect a user who signs a compromised address.
This event highlights why Web3 developers are reassessing how external JavaScript libraries are loaded and trusted.
How Website Owners Can Defend Against Supply-Chain Attacks
Product owners and developers can take practical steps to mitigate third-party software risks:
- Subresource Integrity (SRI): Use SRI hashes to ensure external scripts have not been modified.
- Content Security Policy (CSP): Limit which external domains can execute scripts or receive outgoing data.
- Minimize External Dependencies: Audit and remove unnecessary third-party scripts from sensitive pages like checkout or wallet connections.
- Continuous Monitoring: Implement real-time monitoring tools to detect sudden changes in front-end script behavior.
Practical Steps for Everyday Crypto Users
While developers work on fixing front-end vulnerabilities, users can protect themselves by adopting smart security habits:
- Double-Check Addresses: Always verify every character of a destination address before sending crypto.
- Use Hardware Wallet Displays: Verify transaction details on your physical wallet screen rather than relying solely on the web browser.
- Keep Devices Updated: Maintain current operating system versions to patch known security vulnerabilities.
- Separate Stashes: Avoid storing all digital assets in a single wallet or platform.
Conclusion: Vigilance Remains Essential
The Optimizely incident demonstrates how vulnerable modern web services can be when third-party tools are compromised.
By understanding supply-chain risks and double-checking wallet information, users can stay safer while navigating the Web3 landscape.
Latest blog posts


Trump Meme Coin Dinner Seat Cost Falls to $518
The minimum threshold to qualify for President Donald Trump's meme coin dinner has plummeted from $55,000 to just $518 ahead of tonight's event.
|


Kalshi Faces Potential Nationwide Shutdown in NY Court Battle
Prediction market platform Kalshi faces a crucial court hearing in New York that could force a nationwide shutdown and liquidate user positions.
|
Chainflip Discloses $12M Exploitation Involving 122.9 BTC
Chainflip faced a $12 million exploit involving BTC, ETH, and stablecoins, offering a 10% bounty for the return of funds.
|