

Chainflip Discloses $12M Exploitation Involving 122.9 BTC
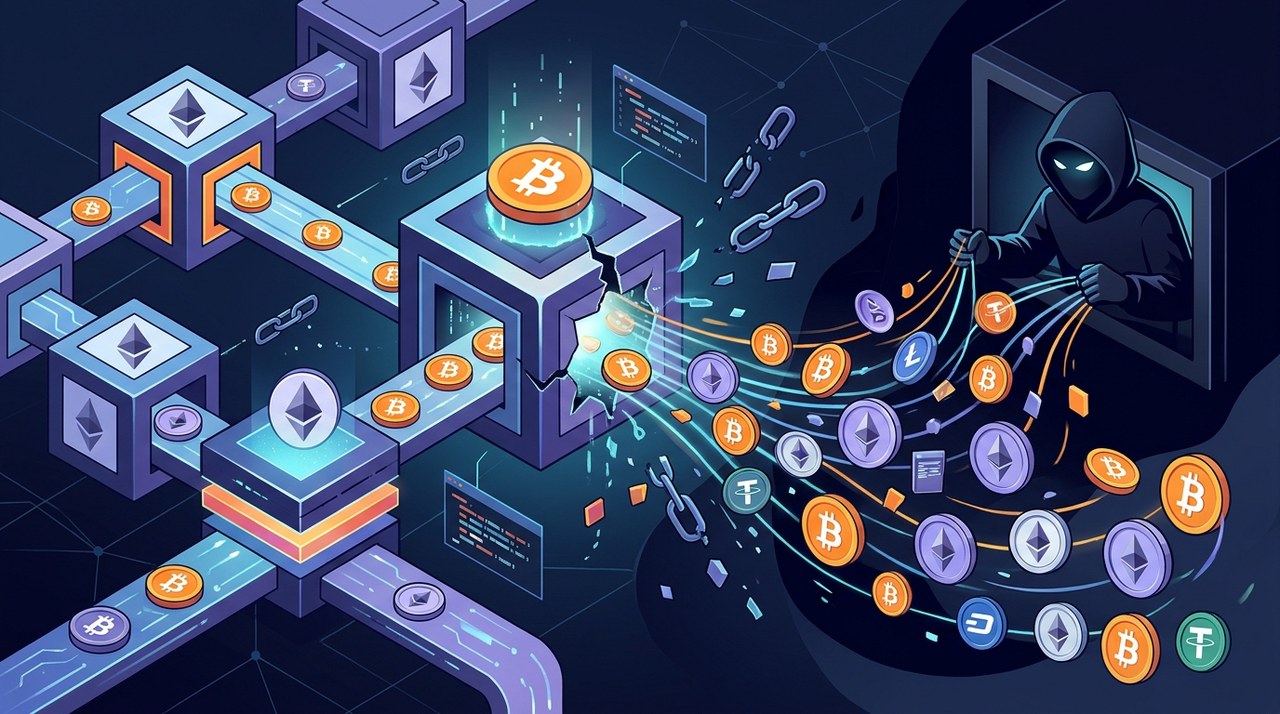
Chainflip Discloses Security Breach and Loss of Stolen Funds
Cross-chain exchange protocol Chainflip has reported a major security incident resulting in protocol losses climbing to $12 million. According to official disclosures, the attacker managed to siphon away 122.9 Bitcoin (BTCBTC+0.59%), alongside substantial amounts of EthereumETH+1.61% and stablecoins from protocol vaults.
In an attempt to recover user assets, the Chainflip team reached out to the exploiter with a public offer. The protocol proposed a 10% bounty on the stolen assets if the hacker agrees to safely return the remaining 90% of the funds by Monday.
How Chainflip Works and Why Cross-Chain Protocols Matter
To understand the impact of this event, it helps to look at what Chainflip does in the crypto ecosystem. Chainflip is a decentralized execution network designed to allow direct swaps between native cryptocurrencies across different blockchains.
Unlike traditional exchanges or wrapping mechanisms, protocols like Chainflip enable trading between native assets such as BTC and ETH directly. However, bridging liquidity across distinct blockchains requires complex smart contracts and specialized vault management.
Breaking Down the $12 Million Exploit
The exploit targeted liquid reserves held within Chainflip's smart contract system. The unauthorized withdrawals resulted in the loss of 122.9 BTC, along with significant pools of ETH and stablecoins, taking total losses to $12 million.
Upon detecting the abnormal fund movements, Chainflip paused relevant protocol components to prevent further capital loss. Emergency interventions allow developers to isolate vulnerabilities, perform forensic analysis, and secure remaining liquidity.
The 10% Bug Bounty Strategy Explained
Offering an attacker a percentage of stolen funds has become a recognized recovery method in decentralized finance (DeFi). In this situation, Chainflip offered the attacker a 10% bounty—worth roughly $1.2 million—if they return the rest of the funds by the Monday deadline.
If the exploiter complies, the protocol agrees to treat the event as a white-hat security contribution and forgo legal action. Communication usually takes place via on-chain transaction messages sent directly to the hacker's public wallet address.
Challenges in Cross-Chain Security
Cross-chain protocols remain primary targets for malicious actors due to the concentration of valuable assets across multiple networks. Building secure interoperability bridges involves navigating several technical hurdles:
- Smart Contract Logic Flaws: Undetected bugs in deposit or withdrawal validation code can be exploited to drain protocol reserves.
- Validator Node Vulnerabilities: Decentralized bridges rely on validator consensus, which can be targeted if keys are compromised.
- Cross-Chain Timing Gaps: Differences in block finality times between blockchains create operational edge cases.
Asset Recovery Efforts and Security Protocols
When breaches occur, Web3 projects collaborate with blockchain analytics platforms to track compromised wallet addresses. Centralized cryptocurrency exchanges are routinely notified to flag and freeze illicit deposits linked to the hack.
While centralized stablecoin issuers can occasionally blacklist stolen tokens on smart contract networks, native assets like Bitcoin cannot be frozen at the protocol layer. This makes voluntary returns or exchange enforcement critical for asset recovery.
Understanding DeFi Risk Management
Incidents of this nature underscore the importance of risk awareness when using decentralized applications. Users interacting with liquidity pools or cross-chain protocols should evaluate smart contract audit reports and security frameworks.
Past performance of digital assets is not an indication of future returns, and historical stability of any decentralized protocol does not guarantee future operational resilience. Traders and investors should maintain realistic expectations regarding protocol security and market volatility.
Looking Ahead for Chainflip
The crypto community is monitoring the Monday deadline to see whether the attacker accepts Chainflip's bounty terms. A successful return would significantly reduce net losses for affected users and protocol reserves.
If the deadline passes without resolution, Chainflip is expected to work with international cybercrime agencies and forensic specialists to track down the stolen assets and address protocol vulnerabilities.
Latest blog posts
Kalshi Faces Potential Nationwide Shutdown in NY Court Battle
Prediction market platform Kalshi faces a crucial court hearing in New York that could force a nationwide shutdown and liquidate user positions.
|
Peter Brandt Links 75% Bitcoin Drops to Past Rallies
Veteran trader Peter Brandt analyzes whether Bitcoin's recent sell-off mirrors past bull market cycles that saw steep pullbacks of 75% or more.
|
Bitcoin Rebounds Above $60K: Can the Price Recovery Hold?
Bitcoin climbed back above $61,000 after hitting a two-month low, as traders weigh short squeezes against persistent market caution.
|