
Was Nvidia Hacked? Ransomware Group Claims Cyber Breach
What Is Happening with Nvidia Right Now?
Recent news reports are raising serious questions across the technology community about the network security status of Nvidia.
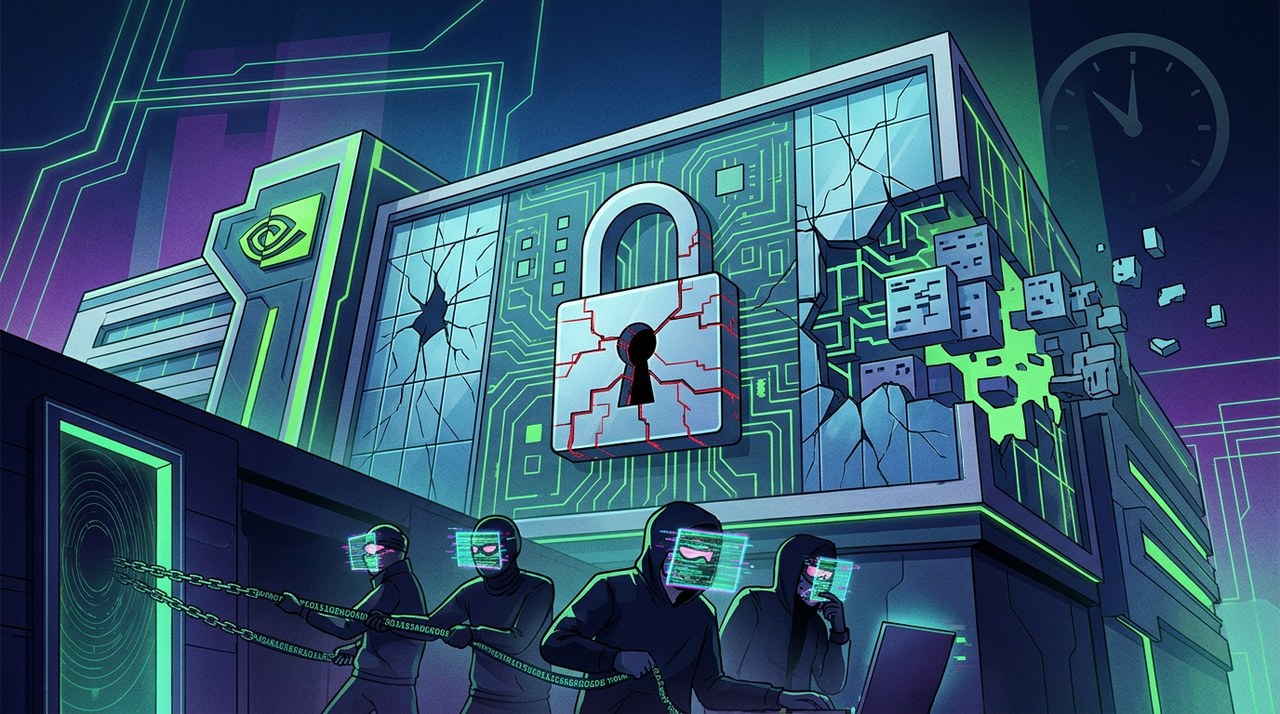
A ransomware group named The Gentlemen recently claimed that it successfully breached the network of the semiconductor giant.
News of this alleged cyberattack first surfaced through International CyberCYBER+7.62% Digest, a widely followed cybersecurity news account.
However, it is essential to emphasize right away that there is currently no public evidence verifying these breach claims.
Inside the Claim: What Was Posted on the Dark Web?
According to cybersecurity monitors, The Gentlemen added Nvidia to their dark web leak site.
The listing featured a "SOON" label alongside a countdown clock set for approximately 10 days.
At this point, the ransomware group has not published any stolen files, code, or private internal documents.
Cybercriminals routinely use public countdown timers to exert maximum psychological pressure on corporate targets.
Understanding Ransomware: How Do These Attacks Work?
Ransomware is malicious software designed to block system access or exfiltrate sensitive files from network servers.
Attackers typically demand a payment, usually in cryptocurrency, in exchange for decrypting data or keeping it private.
In a double-extortion scheme, cybercriminals steal proprietary files before encrypting local computer systems.
If the targeted entity refuses to pay the ransom, the attackers threaten to leak the files to the public.
Is The Claim Real or an Empty Threat?
In the world of threat intelligence, dark web listings do not automatically prove that a security breach took place.
Some extortion groups create placeholder posts simply to gain publicity or create panic among corporate shareholders.
In other instances, threat actors compromise a minor third-party vendor and mistakenly attribute the data to the enterprise target.
Until concrete proof of stolen files is released or Nvidia provides official verification, the claim remains speculative.
Why Nvidia Is a High-Profile Target for Cybercriminals
Nvidia plays a massive role in global technology infrastructure as a primary producer of advanced hardware.
The company produces graphics processing units (GPUs) critical for artificial intelligence development and crypto mining operations.
Because of Nvidia's massive valuation and strategic market presence, hacker groups view it as an attractive victim for extortion.
Any legitimate leak involving proprietary blueprints or source code could pose substantial challenges for the broader tech sector.
Looking Back: Previous Cyber Incidents Involving Nvidia
This is not the first time that Nvidia has been mentioned in connection with major cyber extortion attempts.
In early 2022, an extortion group known as Lapsus$ successfully breached Nvidia's internal corporate systems.
During that previous incident, the group leaked sensitive employee credentials and proprietary software driver details online.
Nvidia responded by enhancing security protocols, upgrading network permissions, and collaborating with law enforcement.
Digital asset markets and technology investors closely track such news because past operational disruptions can impact broader market sentiment.
What Should Tech and Crypto Observers Watch Next?
Security analysts will be tracking the ransomware group's leak site as the 10-day timer counts down.
If The Gentlemen group actually possesses stolen corporate data, they typically release sample files as proof of compromise.
If the countdown expires without any leaked evidence, cybersecurity experts will likely classify the incident as a bluff.
Market participants are advised to follow official corporate communications rather than reacting to unverified dark web claims.
How Major Enterprises Defend Against Ransomware Threats
Modern technology corporations rely on robust multi-layered cyber defenses to guard critical digital assets.
- Enforcing zero-trust network access models to restrict lateral movement.
- Requiring hardware-backed multi-factor authentication across all enterprise accounts.
- Maintaining isolated, encrypted offsite backups for critical operational data.
- Conducting continuous threat monitoring to detect suspicious network traffic in real time.
These security frameworks help organizations contain potential intrusions before severe data loss can take place.
Summary and Conclusion
In summary, ransomware group The Gentlemen has listed Nvidia on its leak portal with a 10-day countdown timer.
No proof of compromised files has been published, and Nvidia has not publicly confirmed any security breach.
Observers should remain objective and rely on verified security reports as more details emerge.
Latest blog posts
Hong Kong Urges Banks to Use AI to Stop Crypto Crime
Hong Kong regulators are pushing banks to deploy artificial intelligence to detect illicit crypto transfers instantly while protecting customer accounts.


Bitcoin ETFs See $2.58B Outflows as BlackRock Leads Exits
Spot Bitcoin ETFs experienced $239.94 million in net outflows on Tuesday, taking total November withdrawals to $2.58 billion as institutional buyers turn cautious.
|
Two Major XRP Funds Post $6M Outflows Near $1 Price Level
Canary Capital and Grayscale recorded $6.14 million in combined outflows on November 17, 2026, despite XRP recovering toward the $1 mark.
|