


Vitalik Buterin Warns AI Could Challenge Crypto Security
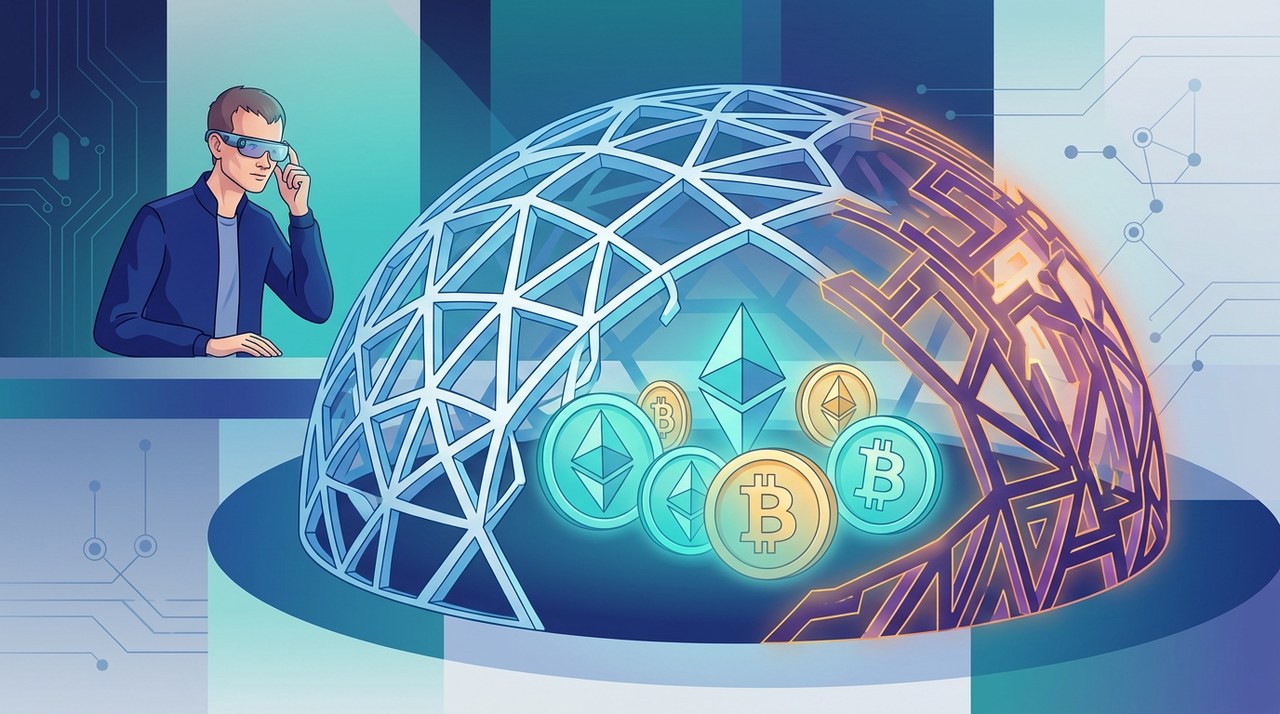
Imagine living in a house with a digital lock that everyone believes is completely unbreakable. Now imagine a supercharged computer coming along that learns how to pick that lock in a fraction of the time experts expected. That is the exact scenario EthereumETH+2.30% co-founder Vitalik Buterin is warning the crypto world about today.
In a recent discussion, Buterin highlighted that rapid advancements in artificial intelligence could weaken key cryptographic defense systems within just two years. Specifically, he pointed to lattice-based cryptography and the Elliptic Curve Digital Signature Algorithm (ECDSA), which currently protects billions of dollars across Bitcoin and Ethereum wallets.
While the news sounds alarming at first glance, Buterin emphasized that holders should not panic or rush to move their funds right away. Instead, he urges developers and researchers to start planning for long-term upgrades before AI catches up with modern encryption standards.
Why Are Cryptographic Defensive Lattices Under Fire?
To understand the concern, it helps to look at how digital security works. For years, the general consensus in computer science was fairly simple: elliptic curve math might eventually become vulnerable to quantum computers, but mathematical models like hashes and lattices would remain bulletproof.
However, Buterin is now questioning the safety of lattice-based math. Because artificial intelligence can process complex mathematical shortcuts at an unprecedented speed, what used to take decades of research could now happen in a matter of months.
I don't recommend anyone scramble to move their funds to new wallets today. But we should take the risks to cryptography from AI-accelerated math seriously, and minimize our exposure to not just quantum-vulnerable cryptography, but also potentially AI-vulnerable cryptography.
Lattice math is not just an abstract concept; it powers real-world defense standards today. For instance, it supports the Module-Lattice-Based Digital Signature Algorithm (ML-DSA), a signature standard designed specifically to resist future quantum computing attacks. It also powers Fully Homomorphic Encryption (FHE), an advanced technique that allows computers to perform calculations on encrypted data without unlocking it first.
To illustrate the risk, Buterin referenced historical code-breaking methods like the number field sieve. Decades ago, researchers discovered mathematical shortcuts for factoring numbers, forcing security teams to continually increase key sizes over time. If AI delivers 50 years' worth of mathematical breakthroughs in just two years, lattice math could face a similar breakdown much faster than expected.
Hashes Offer a Safer Path Forward
If elliptic curves and lattices are facing potential vulnerabilities, where can blockchain networks turn? According to Buterin, mathematical hashes represent a far more durable solution.
Unlike lattices or curves, cryptographic hashes scramble data into fixed codes without leaving a predictable mathematical pattern. Because there is no underlying structure for an AI or quantum computer to exploit, cracking a hash requires brute-force guesswork.
This fundamental difference explains why Ethereum has already been preparing for change. Over the past year, Ethereum's long-term design plan, known as the Lean roadmap, has been shifting toward hash-only security structures. This includes adopting hash-based signature schemes such as SPHINCS and WOTS to protect future transactions.
What About Bitcoin and the 'Satoshi Shield'?
Because Bitcoin relies heavily on the Elliptic Curve Digital Signature Algorithm (ECDSA), it shares the same structural exposure as traditional Ethereum wallets. Ethereum researcher Justin Drake warned that under a worst-case scenario, AI-accelerated breakthroughs could crack ECDSA signatures within months rather than years.
Drake pointed to data from Project11's 'risq list', a public database that tracks Bitcoin public keys already exposed on the blockchain. Interestingly, smaller Bitcoin holders benefit from a unique buffer often called 'Satoshi's shield.'
- What is Satoshi's Shield? It refers to roughly 20,000 exposed blockchain addresses tied to Bitcoin's creator, Satoshi Nakamoto.
- How does it help? Each of these early addresses contains roughly 50 BTCBTC+1.80%. Because these high-value addresses are exposed first, attackers would likely target them long before looking at smaller wallets.
- Partial coverage: As a result, wallets holding less than 50 BTC enjoy a practical cushion while developers work on network upgrades.
In addition to individual users, major industry entities are being urged to upgrade their infrastructure. Drake highlighted that centralized exchanges and institutional custodians, including Binance, Bitbank, Robinhood, Bitfinex, and TetherUSDT+0.00%, have an immediate opportunity to strengthen their offline cold storage setups before potential vulnerabilities arise.
Practical Guidance for Crypto Holders Today
Despite these warning signs, both Buterin and Drake stress that everyday crypto users should not panic. Making impulsive movements with digital assets often introduces human error, which remains a far bigger threat than theoretical AI exploits.
In fact, Buterin shared a personal reflection regarding asset security, noting that he has personally lost more funds due to mistakes during complicated asset transfers than to all actual security hacks combined.
Best Practices Recommended by Experts
- Leave Unused Addresses Alone: If you hold funds in an address that has never broadcasted an outgoing transaction, your public key remains unexposed on the blockchain. Keeping it that way is a simple line of defense.
- Be Careful with Wallet Migrations: Do not rush into moving assets to unfamiliar tools or platforms out of fear, as manual errors cause significant asset losses.
- Multisig Safeguards: For multisig wallets requiring multiple signatures, experts recommend using offchain confirmations. If ECDSA fails, a properly configured multisig setup degrades into requiring a single trusted aggregator rather than leaving funds completely vulnerable to outsiders.
- Privacy Protocols: For privacy-focused applications, sending encrypted notes offchain via private communication channels is strongly preferred over posting encrypted data directly onchain.
A Challenge Beyond Blockchain Technology
The implications of AI-driven mathematical advances stretch far beyond cryptocurrency networks. Modern digital infrastructure relies on public-key cryptography to protect almost every online interaction.
Because hash-only systems cannot handle every single cryptographic task, standard internet tools like virtual private networks (VPNs), secure messaging apps, and standard website SSL encryption all depend on structured mathematics.
To prepare for an era where AI accelerates code-breaking capabilities, Vitalik Buterin offers a straightforward rule of thumb for systems intended to last for decades: multiply existing cryptographic key sizes by 10 today. By increasing key lengths significantly, security engineers can stay well ahead of fast-evolving AI capabilities.
Latest blog posts


Bitcoin Hits $55,000 Low as 4-Year Cycle Theory Comes into Focus
Bitcoin touched $55,081 in November 2026 before recovering above $60,000, leading market analysts to examine historical four-year cycle patterns.
|

3 XRP Ledger Features Race for 2026 Activation
Three key XRP Ledger amendments—Lending Protocol V1_1, Confidential Transfers, and Single Asset Vault—are seeking final validator votes before the end of 2026.
|


Google's Quantum Chip Beats Classical Limits in Impossible Game
Google's latest quantum chip has achieved a historic milestone by outperforming classical supercomputers in a non-local quantum game once deemed mathematically impossible for standard binary hardware.
|