SlowMist Warns of Fake TradingView Crack Stealing Crypto Data
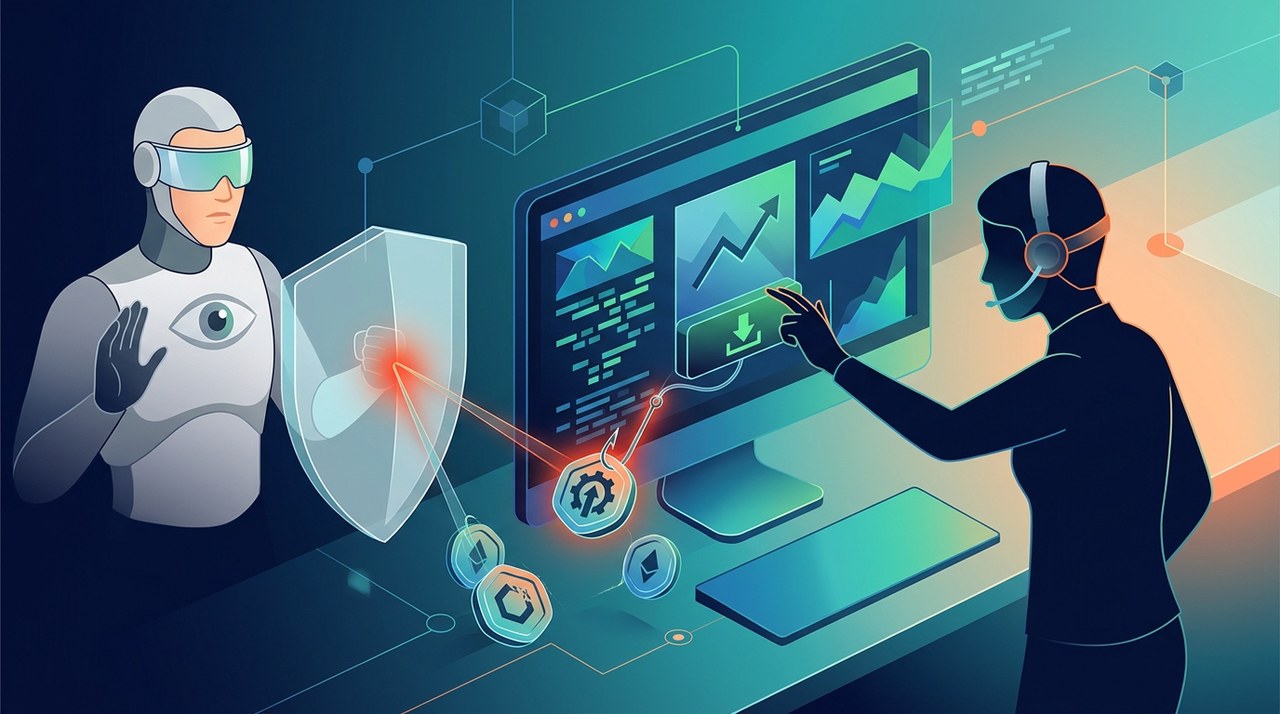
Fake TradingView Premium Software Spreads Infostealer Malware
If you analyze crypto charts, you likely know TradingView as one of the essential tools in the space. However, a security alert shows why trying to get paid charting features for free can cost you your digital assets.
Blockchain security firm SlowMist has issued an urgent warning about a fake version of TradingView Premium. According to security researchers, this fake software has been promoted on X (formerly Twitter) since mid-October.
The download was advertised as a cracked release of TradingView Premium. Instead of granting free subscription features, the file installs dangerous Windows malware designed to steal sensitive data.
The social media campaign gained significant traction before being exposed. One of the main posts offering the free download link generated over 360,000 views.
How the Fake TradingView Premium Trap Worked
The malicious campaign relied on clever social engineering tactics to trick unsuspecting crypto traders.
An account on X operating under the handle Cryptotrice, who claimed to be an on-chain developer, repeatedly published guides promoting a software build.
Cryptotrice shared details about what they described as a reverse-engineered build of TradingView Premium, specifically version 3.3.0 released in October.
The Bait and KeyGen Mechanism
The promotional posts tempted traders with premium capabilities that normally require a paid plan:
- Opening up to 8 charts per browser tab
- Setting up to 400 active price alerts
- Disclaimers claiming the software was for educational purposes only
To access the features, users had to download a password-protected zip file. After opening the archive, victims were instructed to launch the app and click generate inside a KeyGen window.
A KeyGen is a tool created to generate unlicensed activation keys. Attackers often use password-protected files and KeyGens because victims expect security software to flag them, causing users to ignore antivirus alerts.
What the Infostealer Does Behind the Scenes
Security firm SlowMist analyzed the software sample and confirmed it is a fully functional infostealer.
Once executed on a Windows machine, the malware extracts personal credentials and transmits them directly to attackers.
Stolen Credentials and Server Routing
- Web Browser Data: Extracts saved usernames, login passwords, and stored session cookies.
- Cryptocurrency Wallets: Scans for browser extension wallets and local wallet files to steal keys.
- Telegram Information: Harvests account login details and messaging data.
- System Transmission: Uses the native Windows WinINet interface to send stolen files to a command-and-control server.
SlowMist found that the malware uses platforms like Telegram and Steam to retrieve and rotate command-and-control server paths. This technique helps the software avoid standard network detection.
The file download link directed users to a domain named arche-hypnose[.]com. Researchers noted that this was a real, legitimate website that hackers compromised to serve malicious files.
Red Flags, False Claims, and Mac Status
A closer look at the campaign shows several major warning signs that point to fraud.
Cryptotrice repeatedly claimed the software was open source and pointed users toward GitHub. However, SlowMist discovered that the actual download links in the posts did not lead to GitHub.
When a follower asked why the GitHub project and Discord server were only accessible inside the desktop app, Cryptotrice gave suspicious excuses.
The promoter claimed the code repository had gone private and insisted that in-app links expired after one use.
In one post reply, a user asked AI tool Grok if the program was safe. Cryptotrice replied directly, making deceptive claims about safety.
Cryptotrice claimed the cracked software was actually safer than official TradingView because absolutely no credentials like emails or passwords ever leave your system.
Status of the macOS Version
SlowMist successfully retrieved and examined the Windows build. However, the macOS link returned a 404 error during analysis.
Because researchers could not obtain a working sample for Mac, SlowMist could not confirm whether macOS devices were targeted by the same malware.
Action Steps for Affected Users
If you downloaded or ran this cracked file, security experts recommend taking immediate action to protect your accounts.
- Disconnect your computer: Immediately unplug ethernet cables and turn off Wi-Fi to stop ongoing data transfers.
- Secure your crypto assets: Use a completely clean, uninfected device to create a new wallet with a new seed phrase, then transfer all funds immediately.
- Reset all account passwords: Change passwords for centralized crypto exchanges, email accounts, and web browsers.
- Terminate active sessions: Update your Telegram password and force-close all active messaging sessions across devices.
Wider Threats: KeyGens and the DarkSword Exploit
Security specialists emphasize that downloading cracked programs carries severe risks for anyone managing crypto.
Cracked software, KeyGens and password-protected archives are among the most common ways infostealers are distributed. Don't install them.
This security advisory comes shortly after another major alert issued by SlowMist regarding mobile devices.
SlowMist recently warned iPhone users about an exploit called DarkSword. That exploit was capable of extracting wallet files and recovery seed phrases from iOS devices when users visited compromised websites.
Whether trading on desktop or mobile, keeping software updated and avoiding cracked files remain critical safeguards for securing your funds.
Latest blog posts


 +2
Bitcoin Reclaims $60K After Dropping to Two-Year Low
Bitcoin bounced back above $60,000 after falling to $55,326, while major altcoins also recovered following heavy sell-offs.
|

Arthur Hayes Receives $306K in VVV as Token Targets Rebound
BitMEX co-founder Arthur Hayes received 15,000 VVV tokens following his $40 price prediction as VVV reclaims key technical indicators above $22.
|
Bitcoin Reaches $55K: Is a Market Bottom Forming?
Bitcoin recently fell to $55,000, prompting market analysts to examine key cycle metrics, seller capitulation, and historical patterns for bottom signals.
|