
Ethereum Bug Fixed Ahead of Major Glamsterdam Upgrade
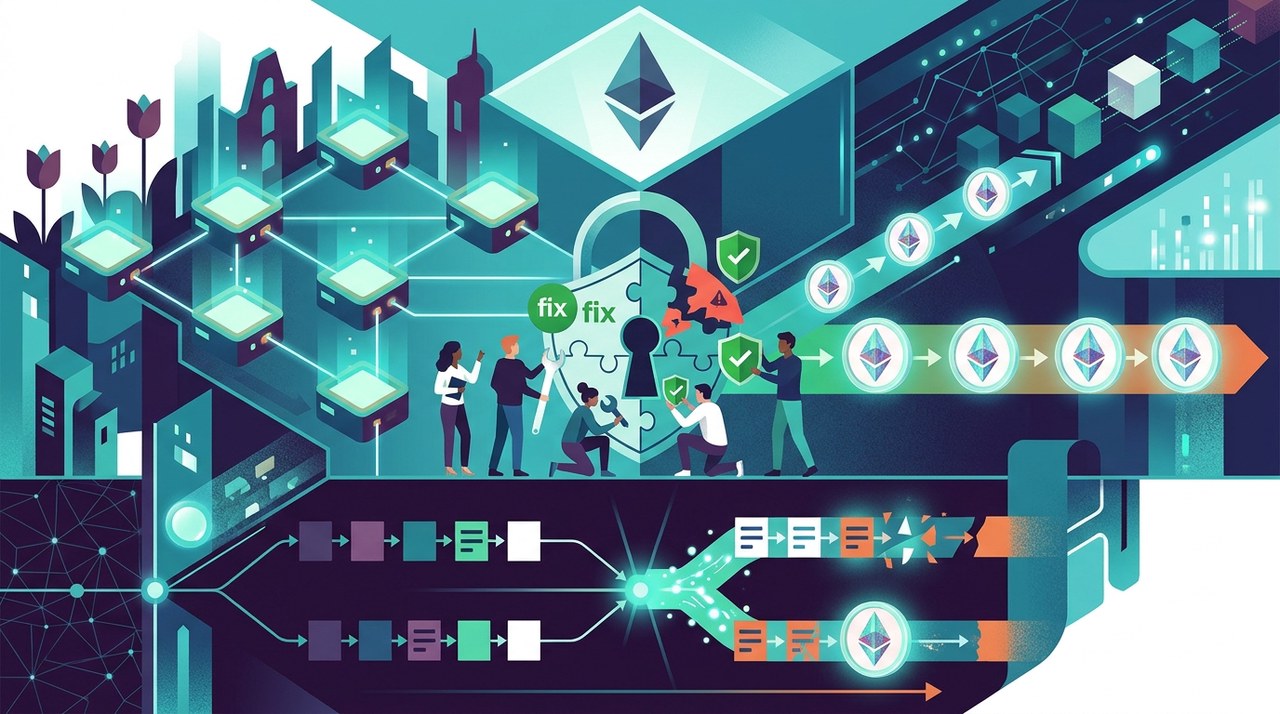
EthereumETH-4.08% Developers Fix Validator Cache Vulnerability
Ethereum developers have resolved a sneaky technical glitch before it could cause real trouble. On November 13, 2026, reporter Arman Shirinyan highlighted a GitHub pull request showing a merged security fix for an Ethereum consensus client.
The patch solves a validator pubkey cache poisoning attack vector. It specifically addresses a vulnerability around the Gloas fork, which serves as the consensus layer component for the upcoming Glamsterdam upgrade.
Without this fix, the bug could cause certain network nodes to reject valid signatures during a fork. As a result, affected nodes would split off from the main blockchain.
Three Deposits and Two Chains: How the Bug Worked
The core problem comes down to how consensus clients handle data caching. Clients store validator public keys and their matching index numbers inside a global cache to speed up processing.
Normally, finalized deposits produce identical validator lists across all network chains. However, edge cases can appear right at a fork boundary.
To exploit this vulnerability, an attacker would need three pending deposits lined up right before the fork occurs:
- Deposit 1: A large balance top-up for an existing network validator.
- Deposit 2 (Key A): A brand-new public key carrying builder credentials.
- Deposit 3 (Key B): A brand-new public key carrying regular validator credentials.
On the canonical (main) chain, the top-up deposit consumes the available balance limit. Because of this, Key A and Key B get processed right after the fork. Key A becomes a builder, while Key B receives the next standard validator index.
However, an attacker could set up a secret side chain where the topped-up validator gets slashed right before the fork. That slashing skips the top-up deposit entirely.
Skipping the deposit allows Key A to get processed earlier on the side chain, taking over Key B's intended index position. The buggy global cache assumed both chains created identical lists, saving Key A across the global system.
When the fork boundary arrived, nodes with the corrupted cache would reject valid signatures from Key B on the main chain and accidentally fork off.
Fortunately, executing this attack requires precise timing, a side chain, and a controlled slashing event. Because of this complexity, the bug was very unlikely to happen by accident.
How the Patch Resolves the Issue
The new update changes when key data gets saved to memory. The client now waits to add keys to the global pubkey cache until their activation eligibility epoch is fully finalized.
Developers also created a new feature called the Head Pubkeys structure. This mechanism combines keys from the head state and the global cache together.
Thanks to this addition, nodes will not lose track of keys even if the chain finalizes without generating new blocks.
What Happens Next?
It is not yet confirmed whether other Ethereum consensus client teams experienced this same caching flaw.
As the Glamsterdam upgrade gets closer, developers are actively searching for and fixing tricky edge cases to protect the network.
You can follow market trends for Ethereum (ETH) as updates progress. Past performance of digital assets is no guarantee of future results.
Latest blog posts

Thailand Proposes $148,000 Cap on Stablecoin Transfers
Thailand is considering draft rules setting a $148,000 daily cap on certain stablecoin transfers and restricting transactions to self-owned wallets.
|

JPMorgan Increases Holdings in Bitcoin ETF and Strategy
JPMorgan reported a 36% increase in Strategy shares alongside 11.4 million BlackRock Bitcoin ETF shares in Q3.
|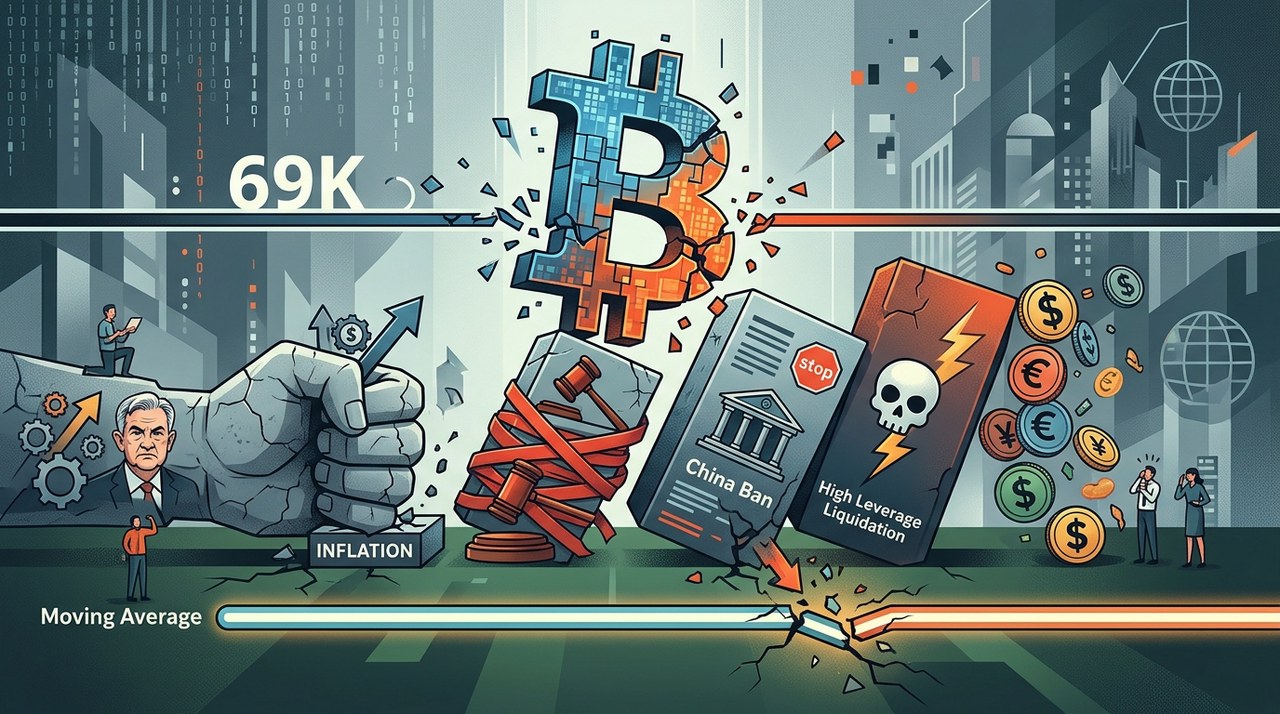
Why Did Bitcoin Drop Below $69,000? 5 Major Factors Explained
Bitcoin fell below $69,000 as rate hike fears, ETF outflows, index changes, and forced liquidations combined in a single week.
|